![logo-horizontal_w.png]](https://support.tiled.co/hs-fs/hubfs/logo-horizontal_w.png?height=30&name=logo-horizontal_w.png)
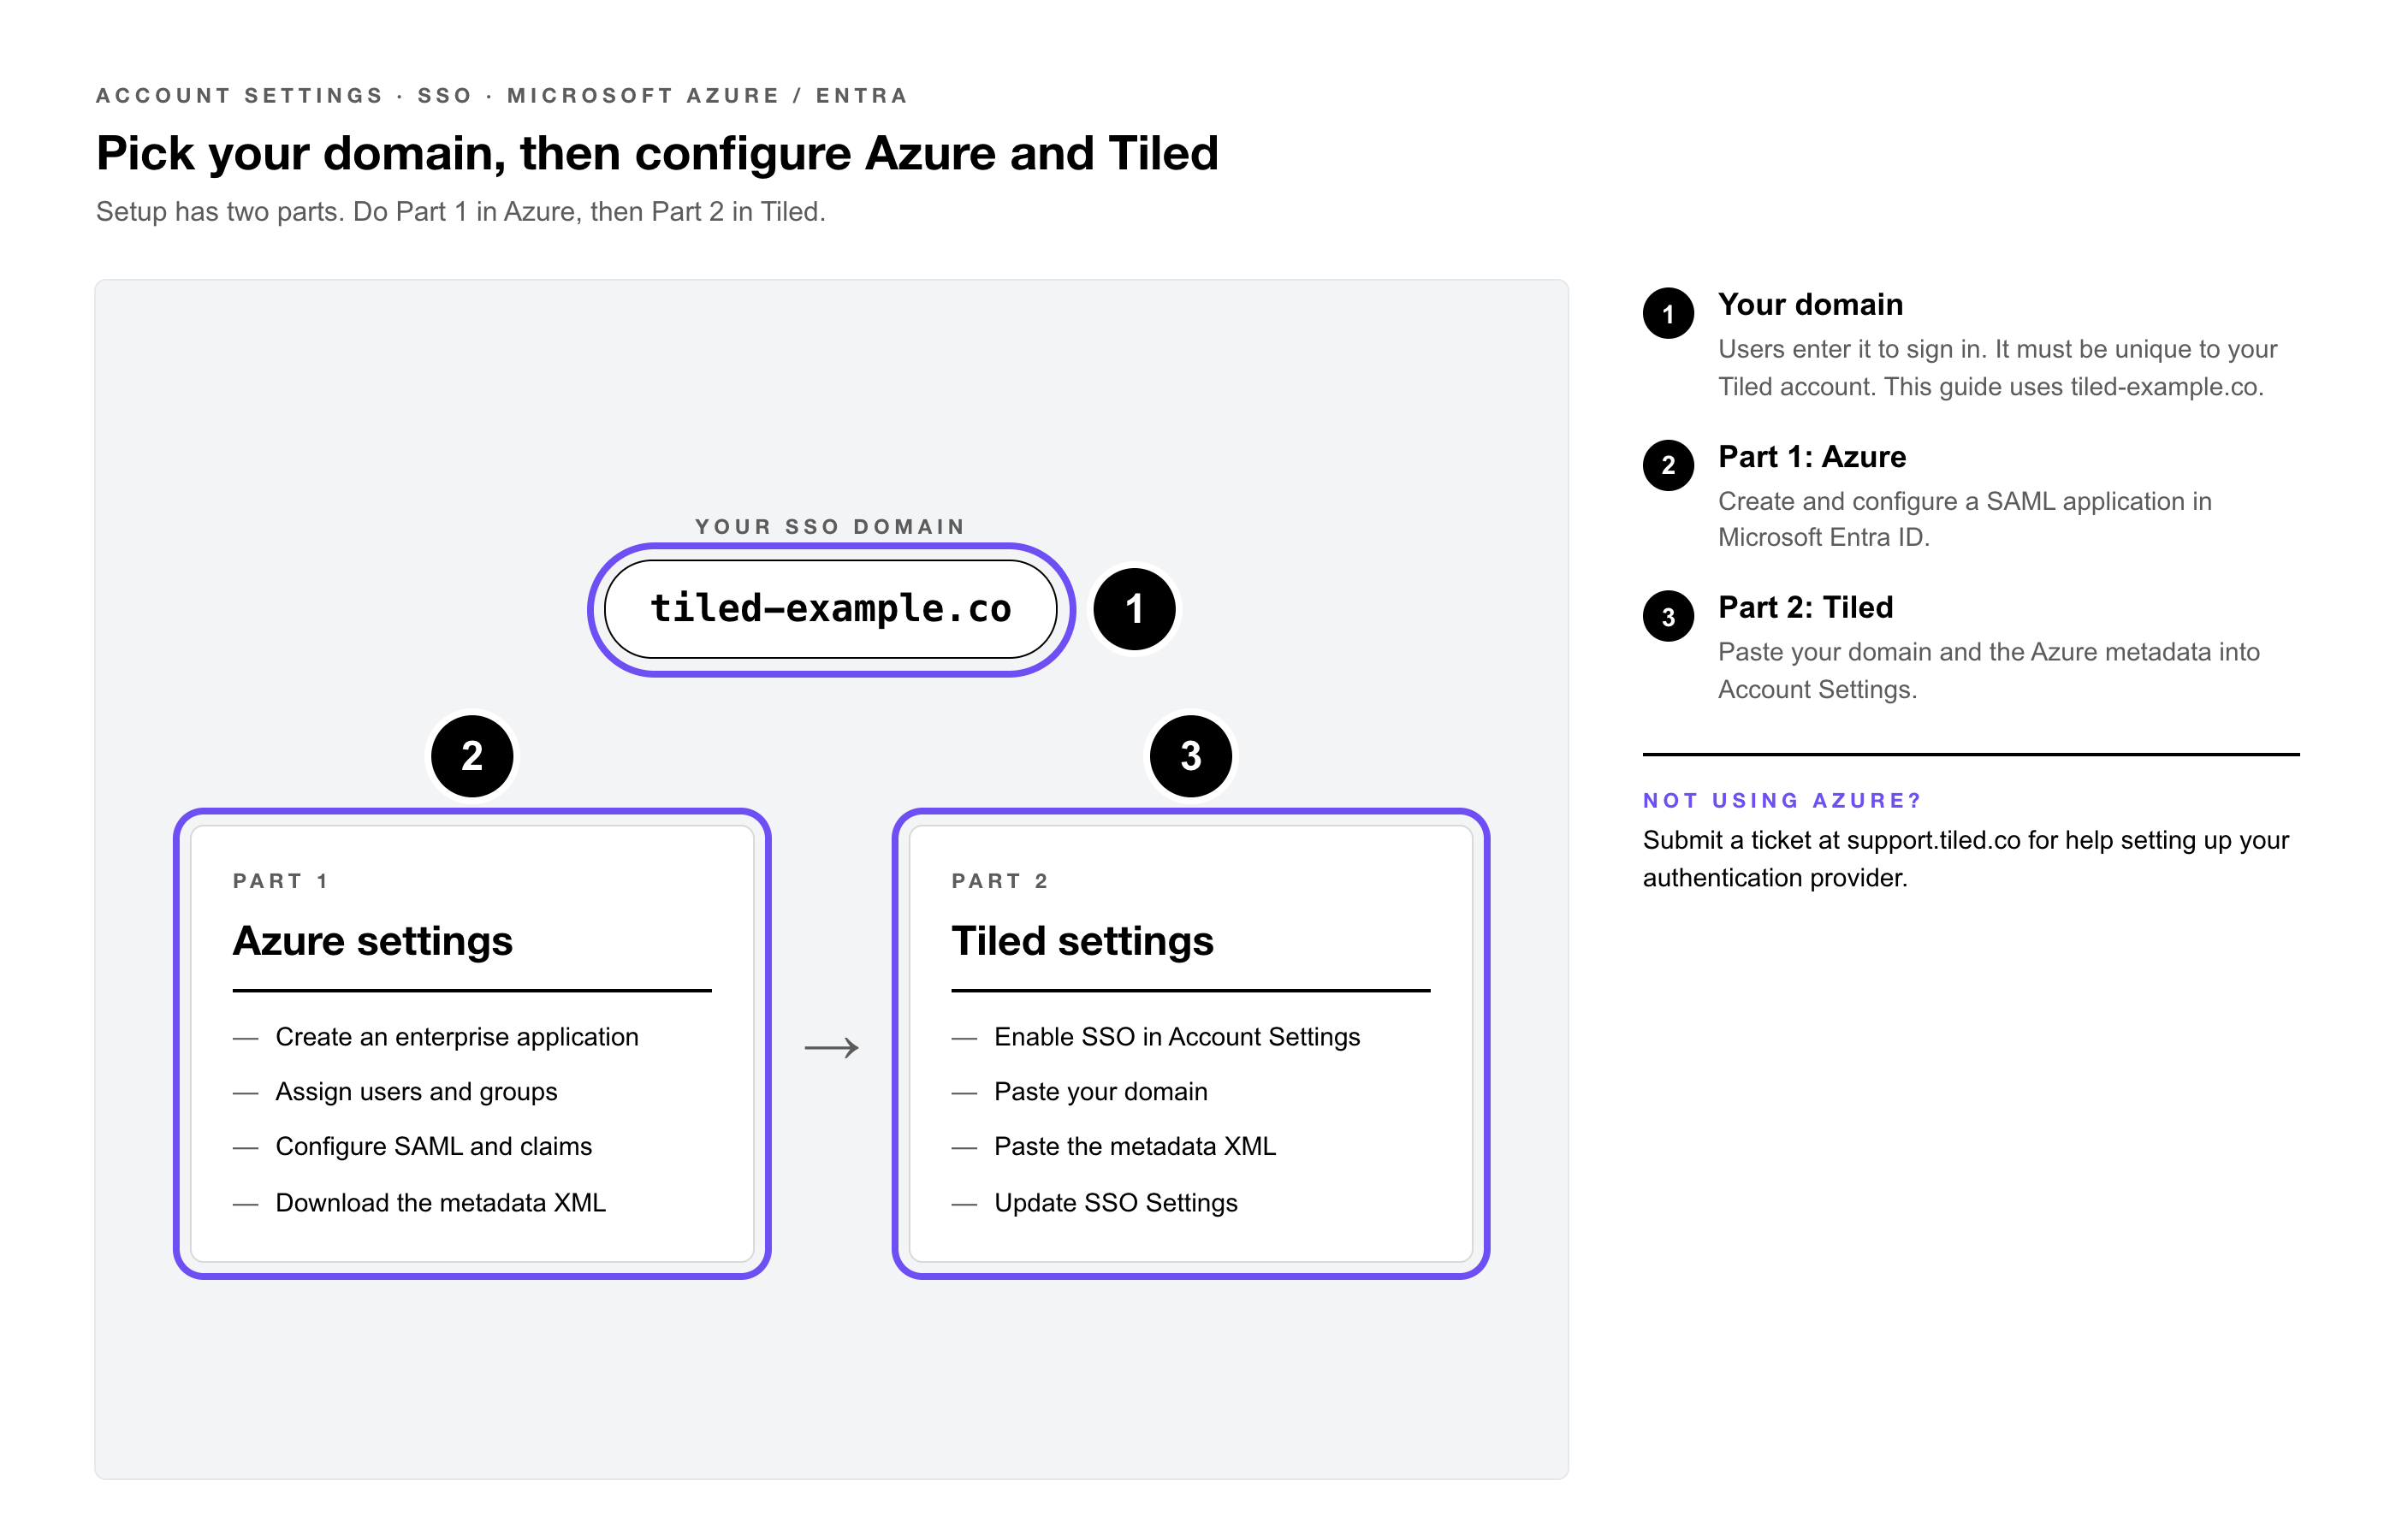
Configuring Azure SSO for Tiled is split into two parts. The first part details how to configure the settings in Azure Account and the second part covers how to configure the settings in Tiled.
Before You Start
|
You Need |
Details |
|
Tiled |
The Account Admin role. |
|
Microsoft Entra ID |
A role that can create enterprise applications, such as Cloud Application Administrator or Application Administrator. |
|
A sign-in domain |
The domain your users enter to sign in, usually your email domain, such as example.com. It must not be used by any other Tiled account. |
|
SSO or Sign in with Microsoft?: Anyone can use Sign in with Microsoft on the Tiled login screen with no setup. SAML SSO, described here, is for organizations that want Entra ID to control who can sign in, require SSO for everyone, or create Tiled accounts automatically. |
First, decide which domain users will enter to authenticate to your Tiled account. In this document, we will use tiled-example.co. This domain must be unique to your Tiled account.
Part 1: Create the Application in Microsoft Entra ID
Create the application
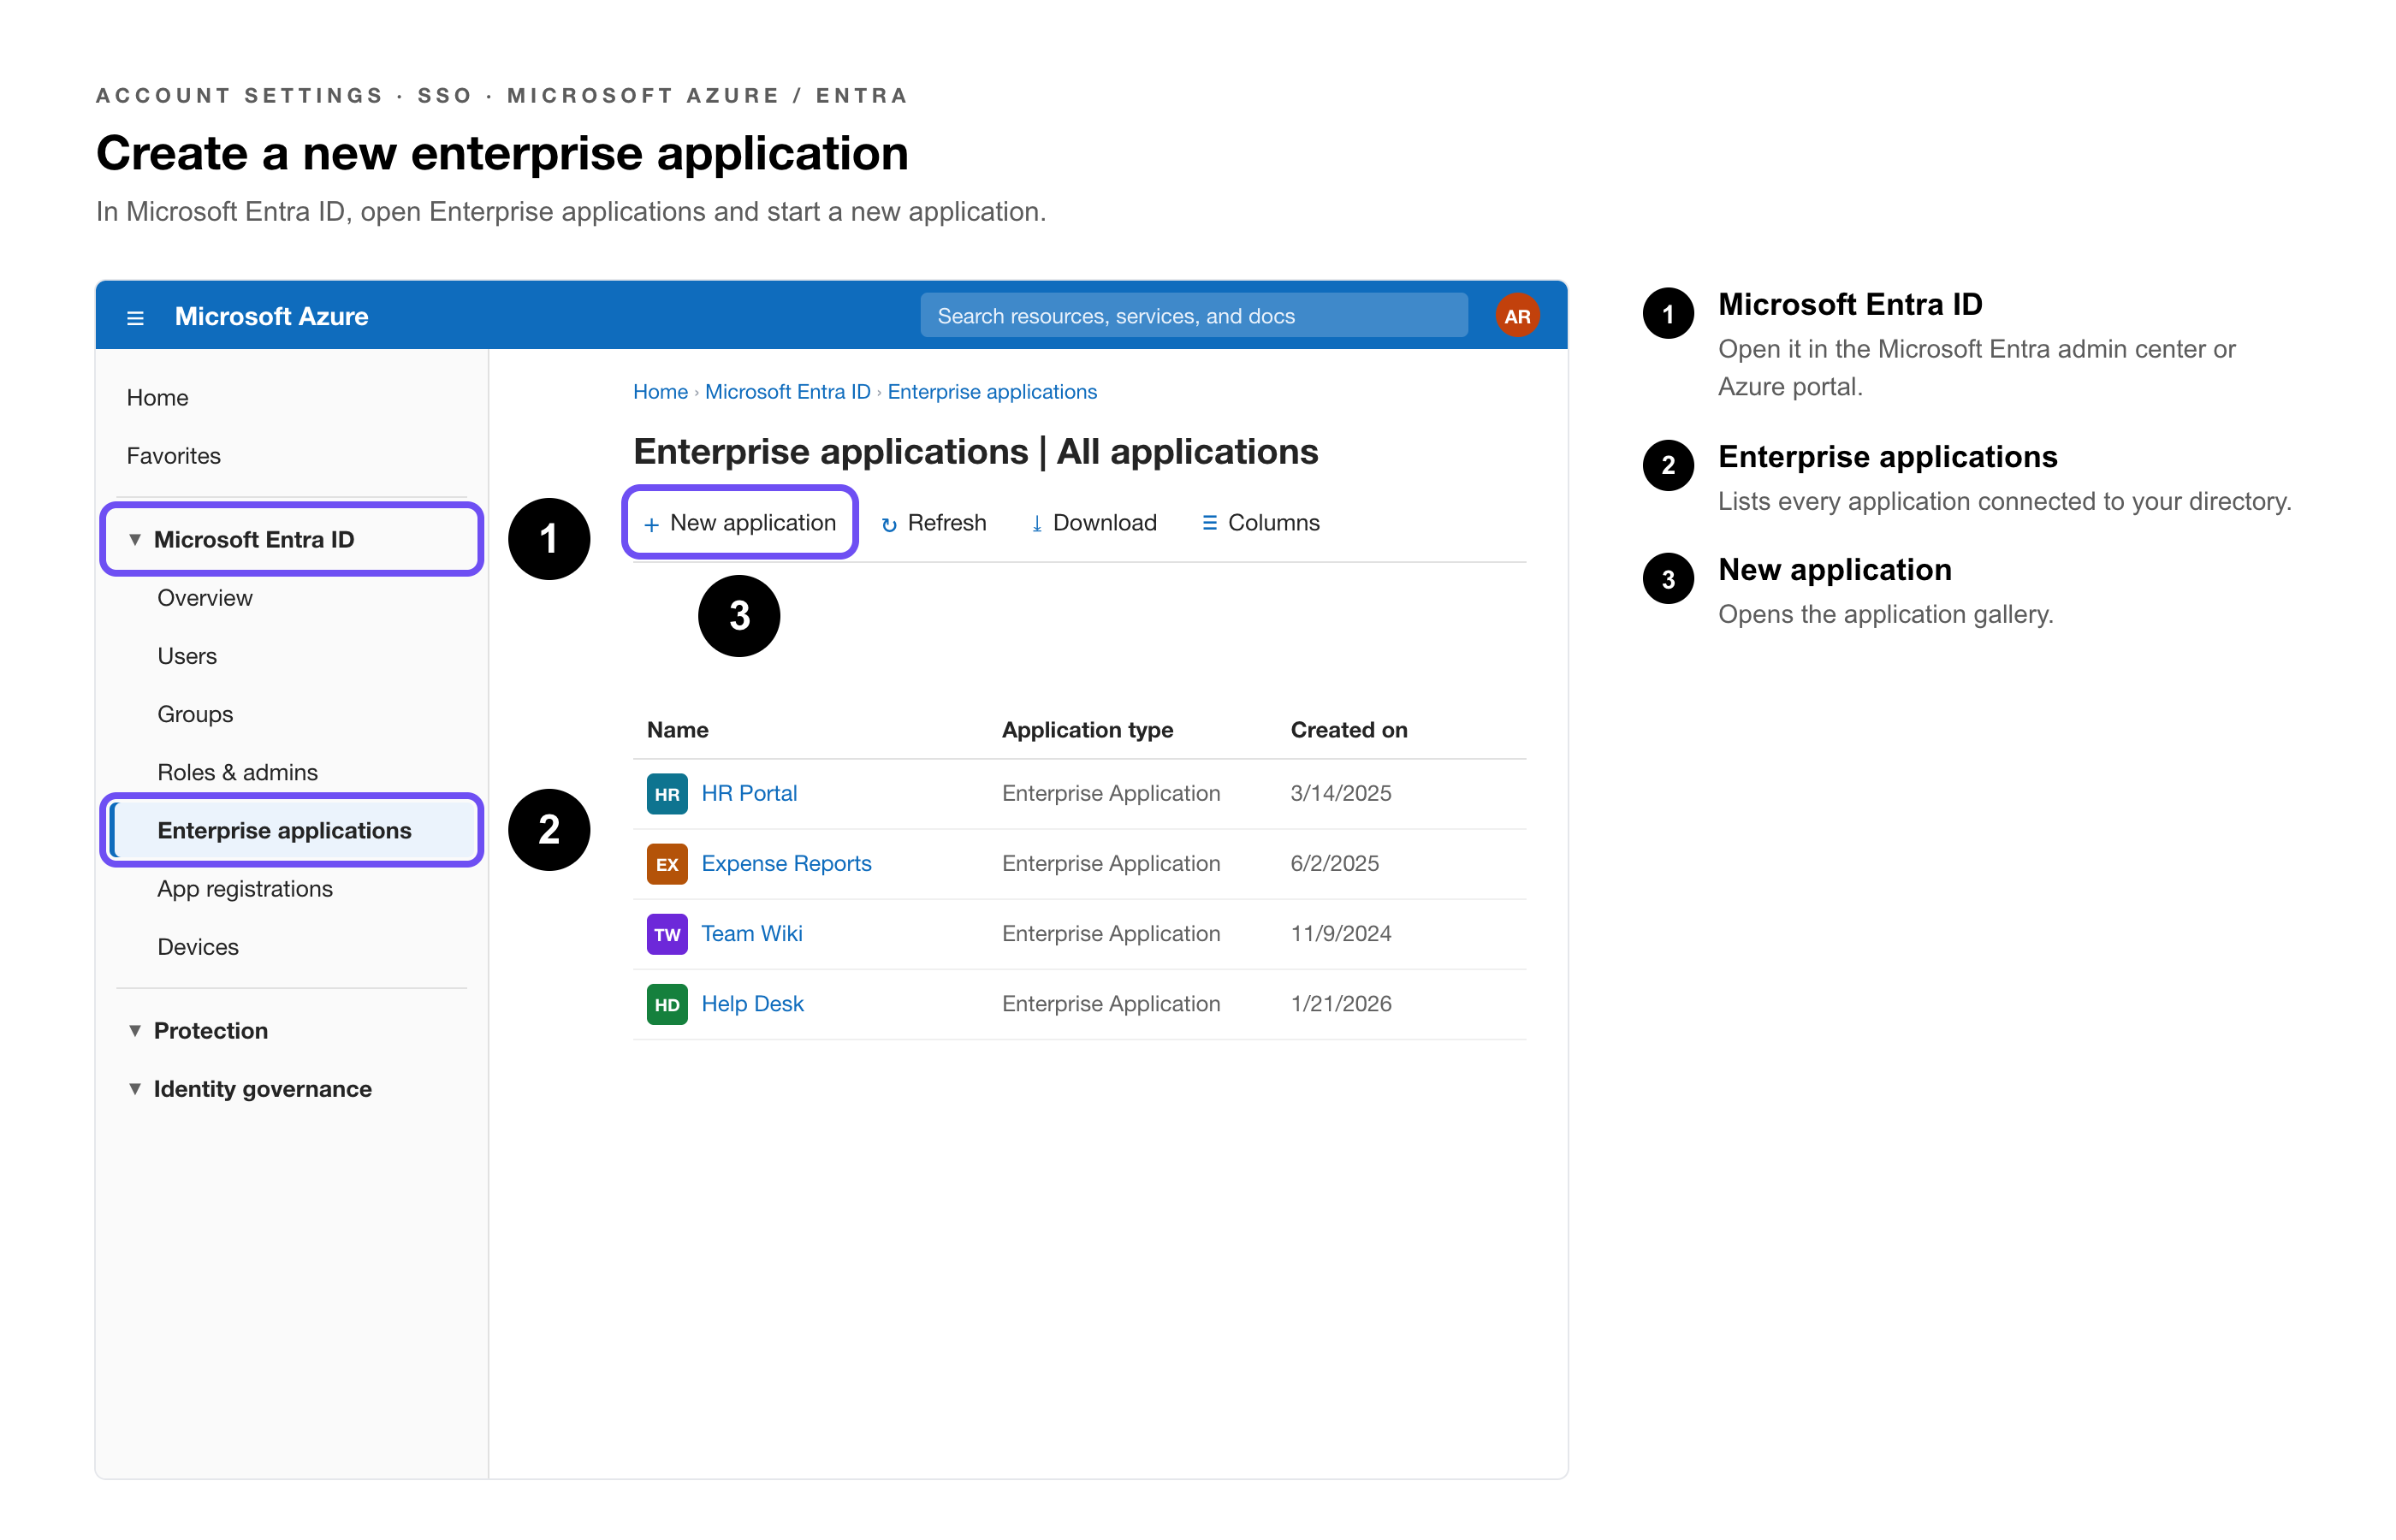
1. Sign in to the Microsoft Entra admin center — and go to Entra ID → Enterprise apps.
2. Select New application, — then Create your own application.
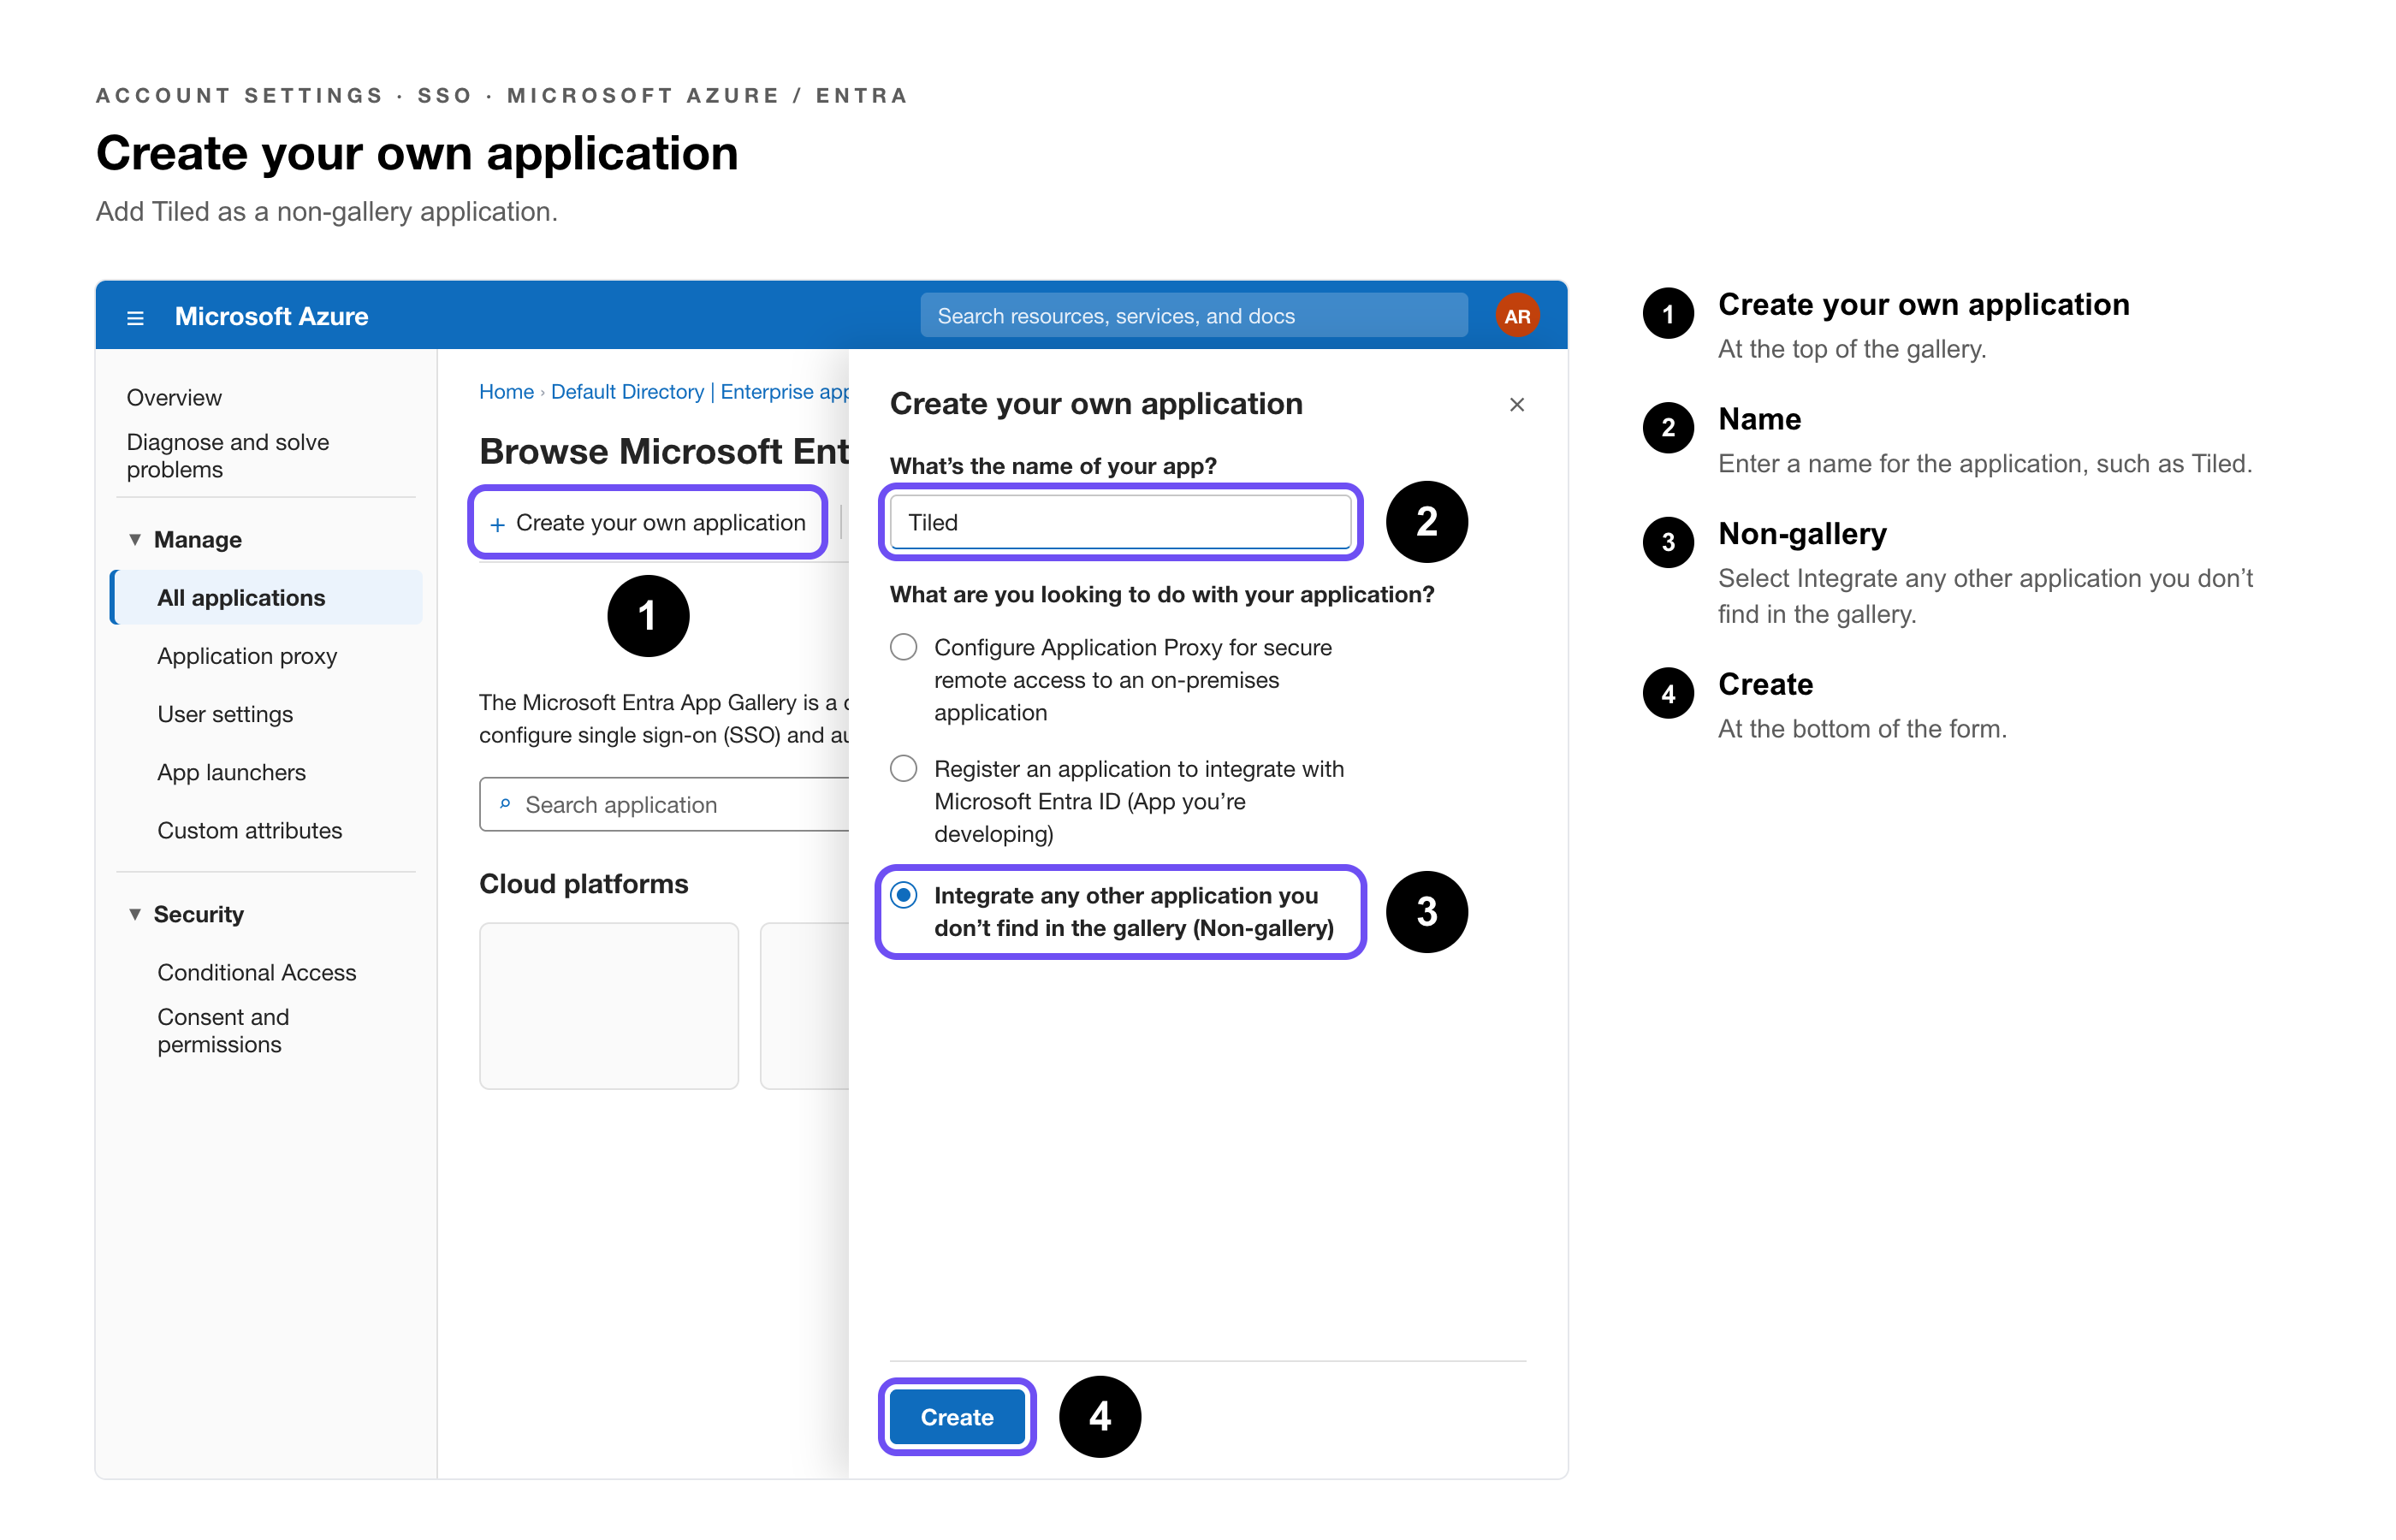
3. Name the application, — for example Tiled, and select Integrate any other application you don’t find in the gallery (Non-gallery). Select Create.
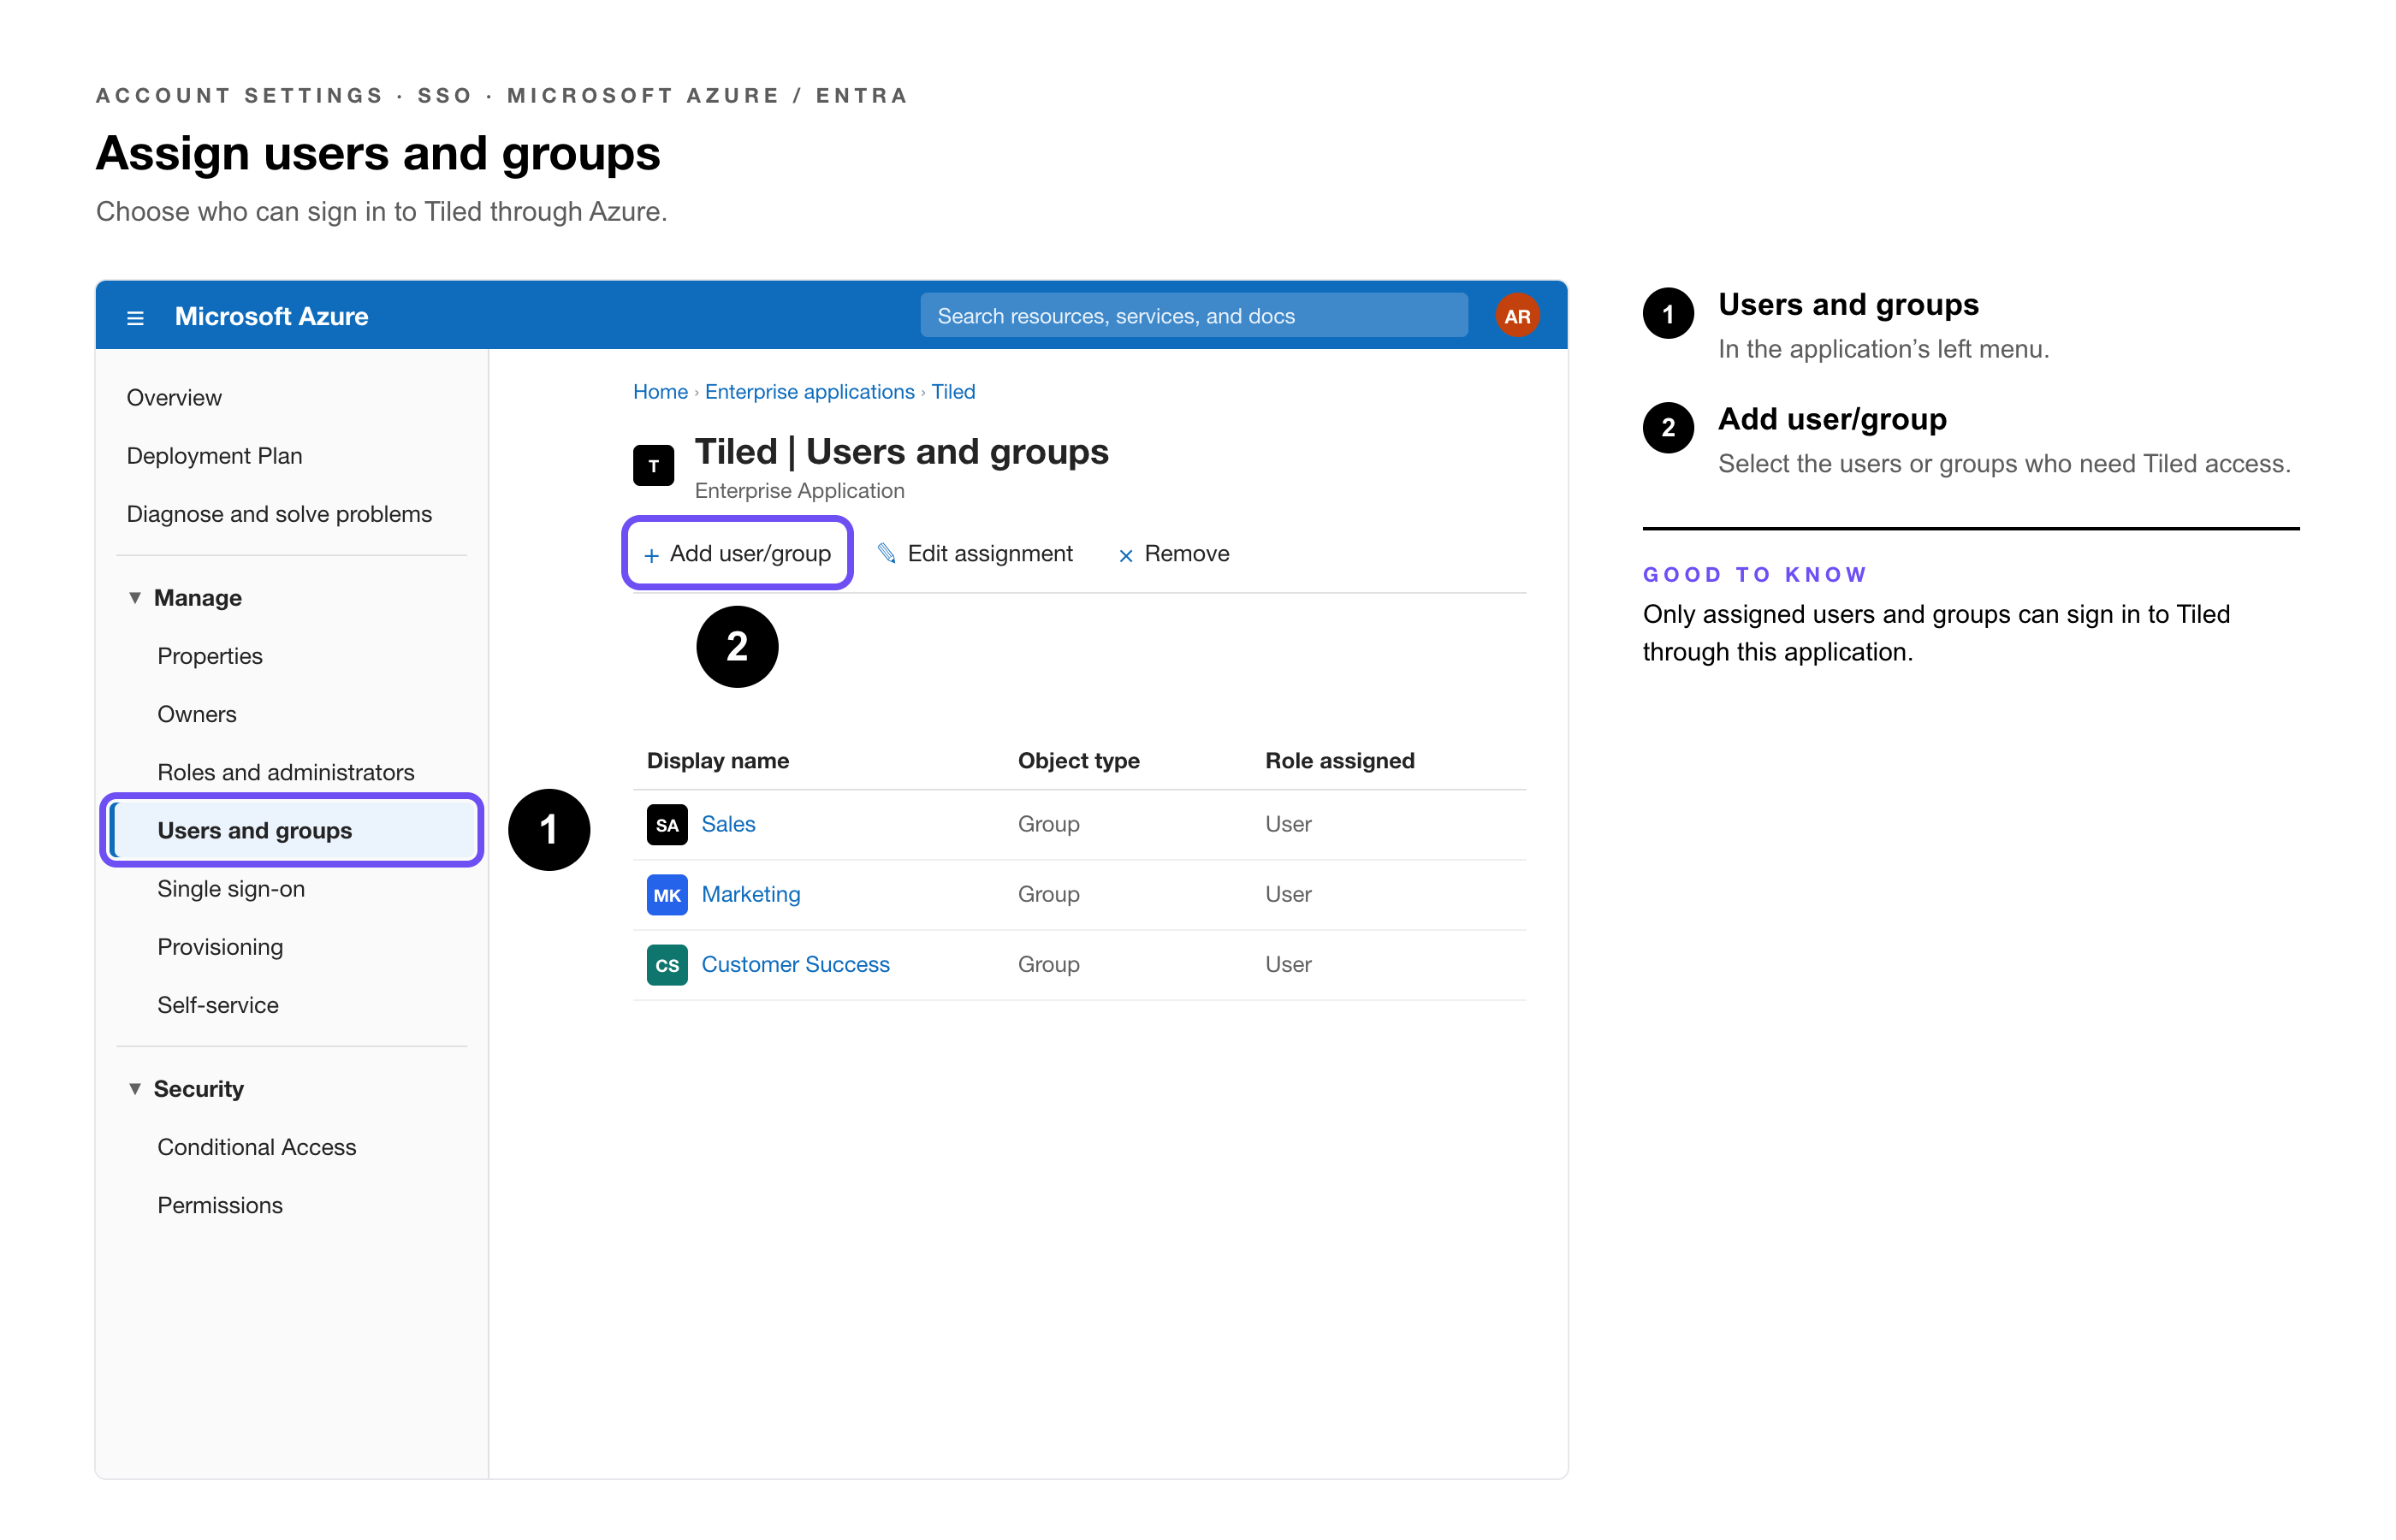
4. Assign people. — Select Users and groups, then Add user/group, choose who should have access to Tiled, and select Assign.
|
Pro Tip: Assign a group, such as “Tiled Users,” rather than individuals. Adding someone to the group in Entra ID is then all it takes to give them access. |
Set up SAML
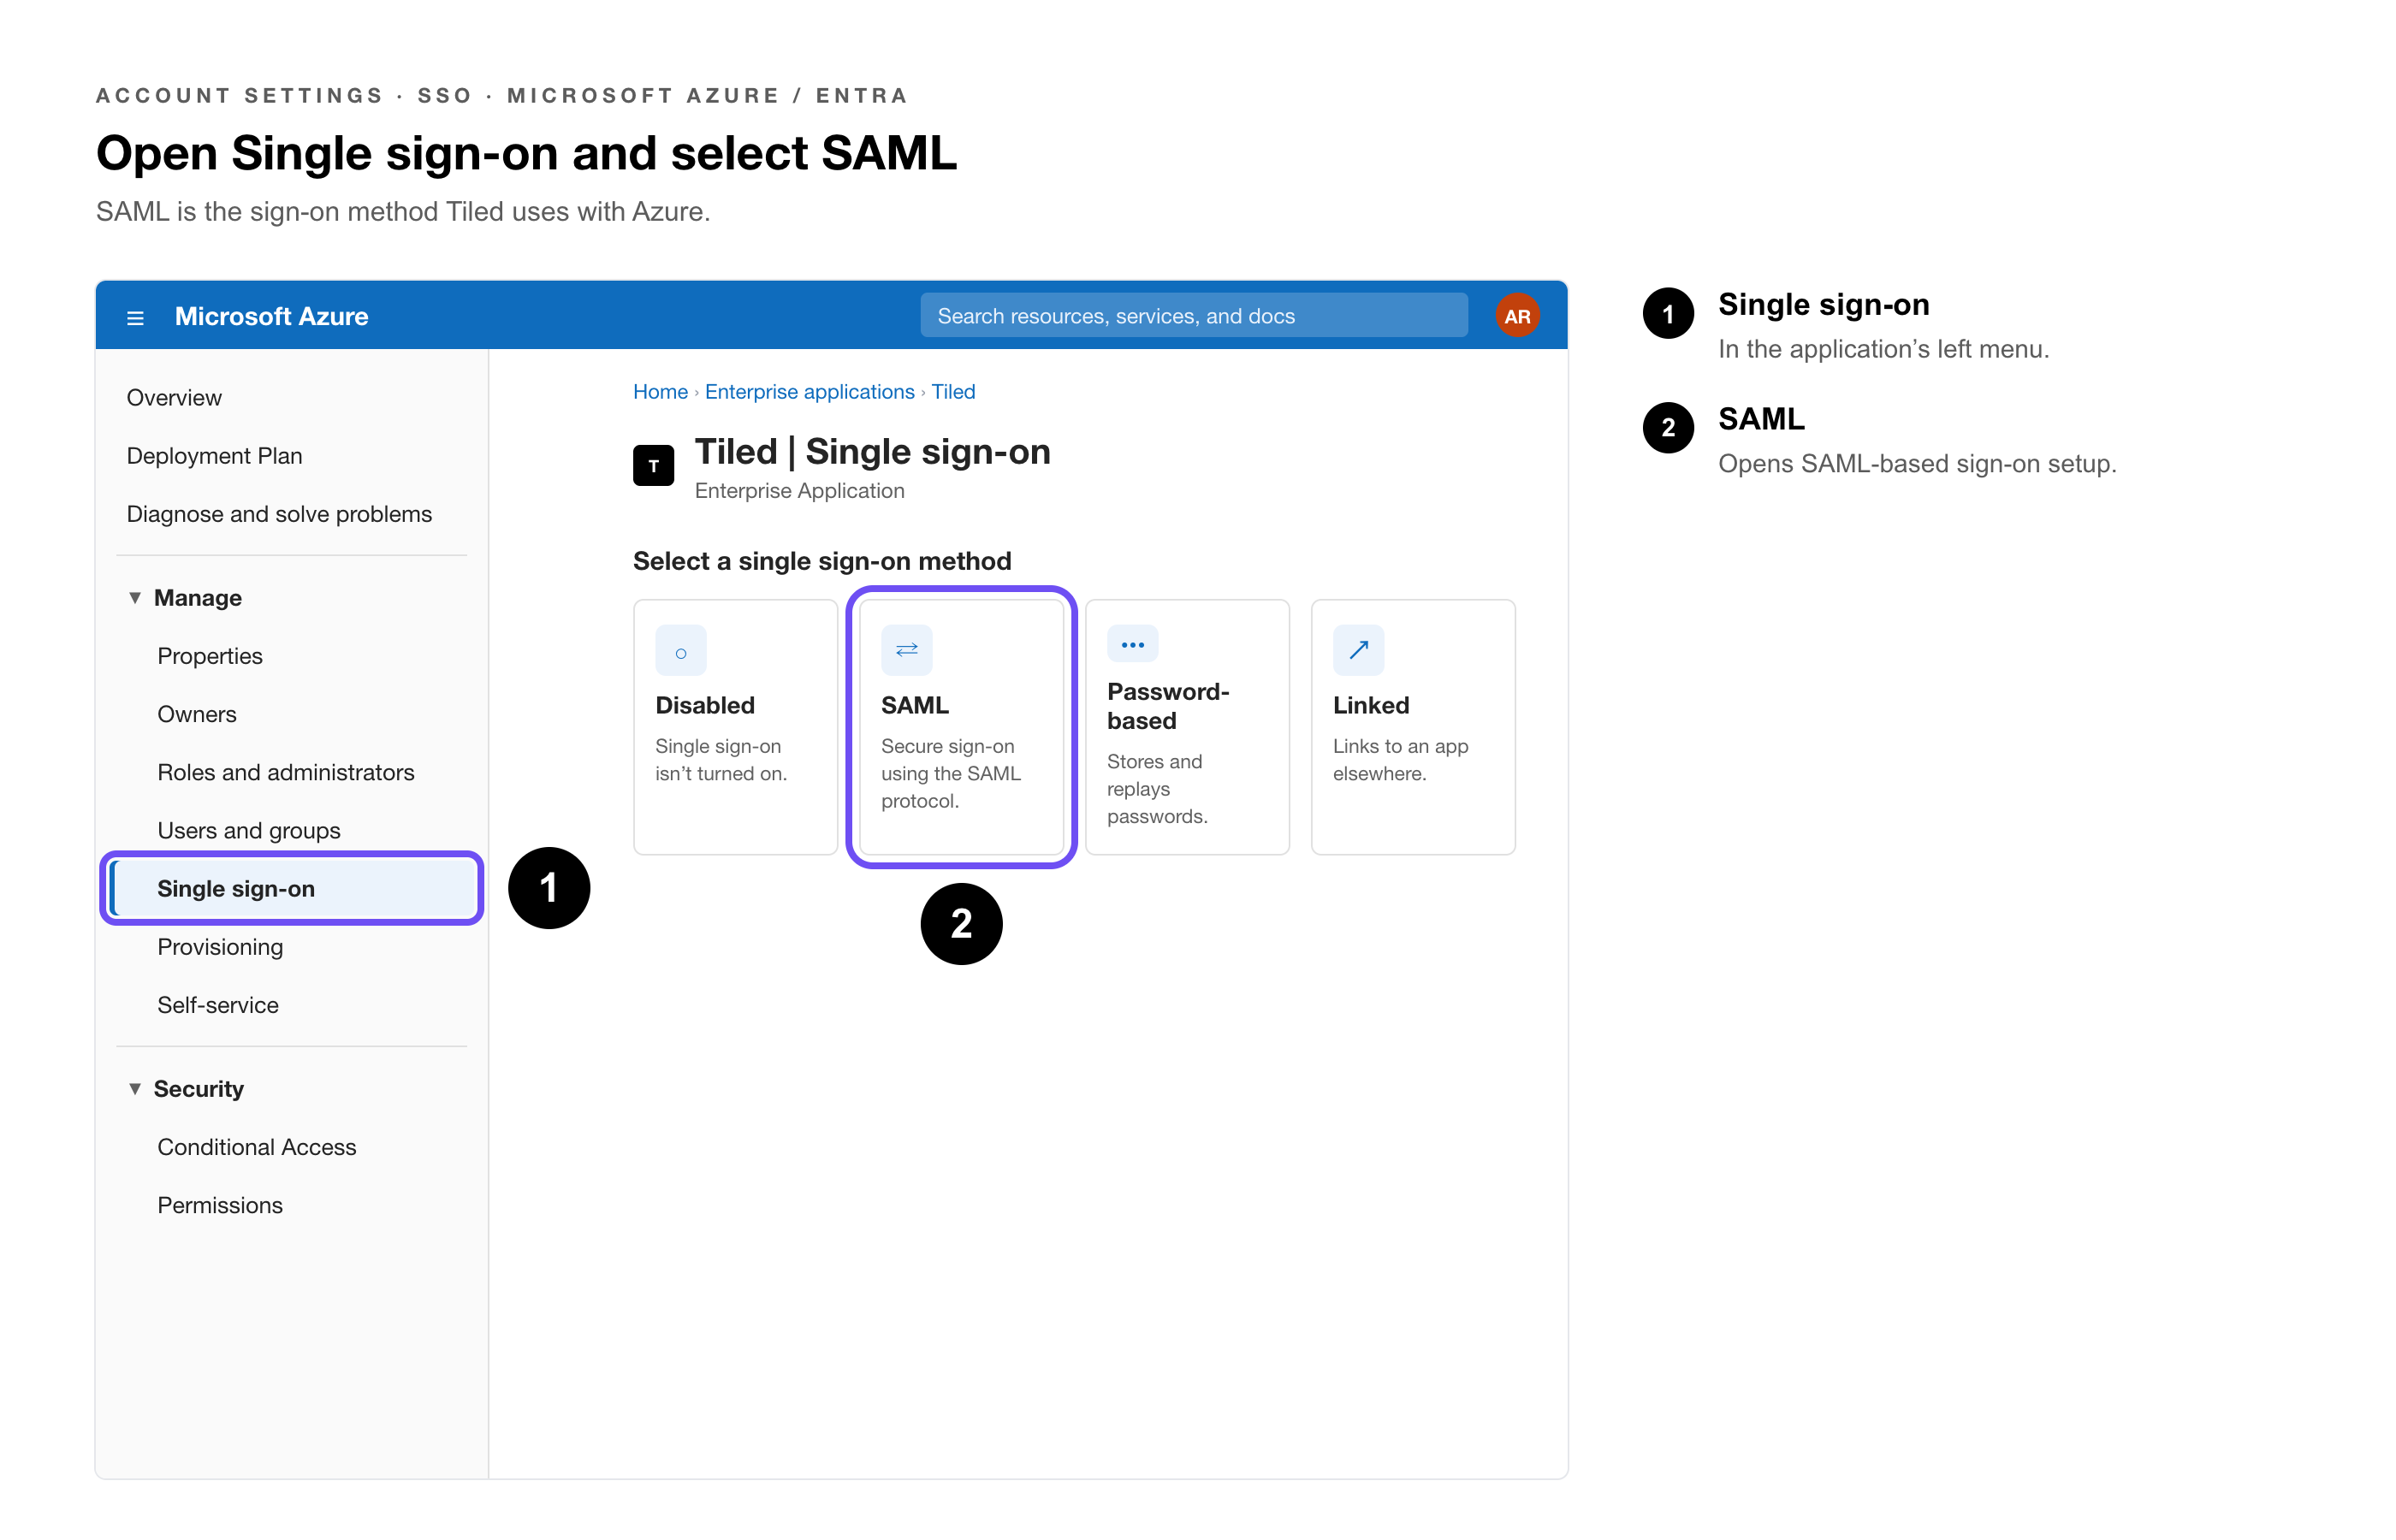
1. Select Single sign-on, — then SAML.
2. Edit Basic SAML Configuration — and enter these values, replacing example.com with your sign-in domain:
|
Field |
Value |
|
Identifier (Entity ID) |
https://api.tiled.co/v2/auth/device/saml2/example.com/metadata.xml |
|
Reply URL (Assertion Consumer Service URL) |
https://api.tiled.co/v2/auth/device/saml2/example.com/assert |
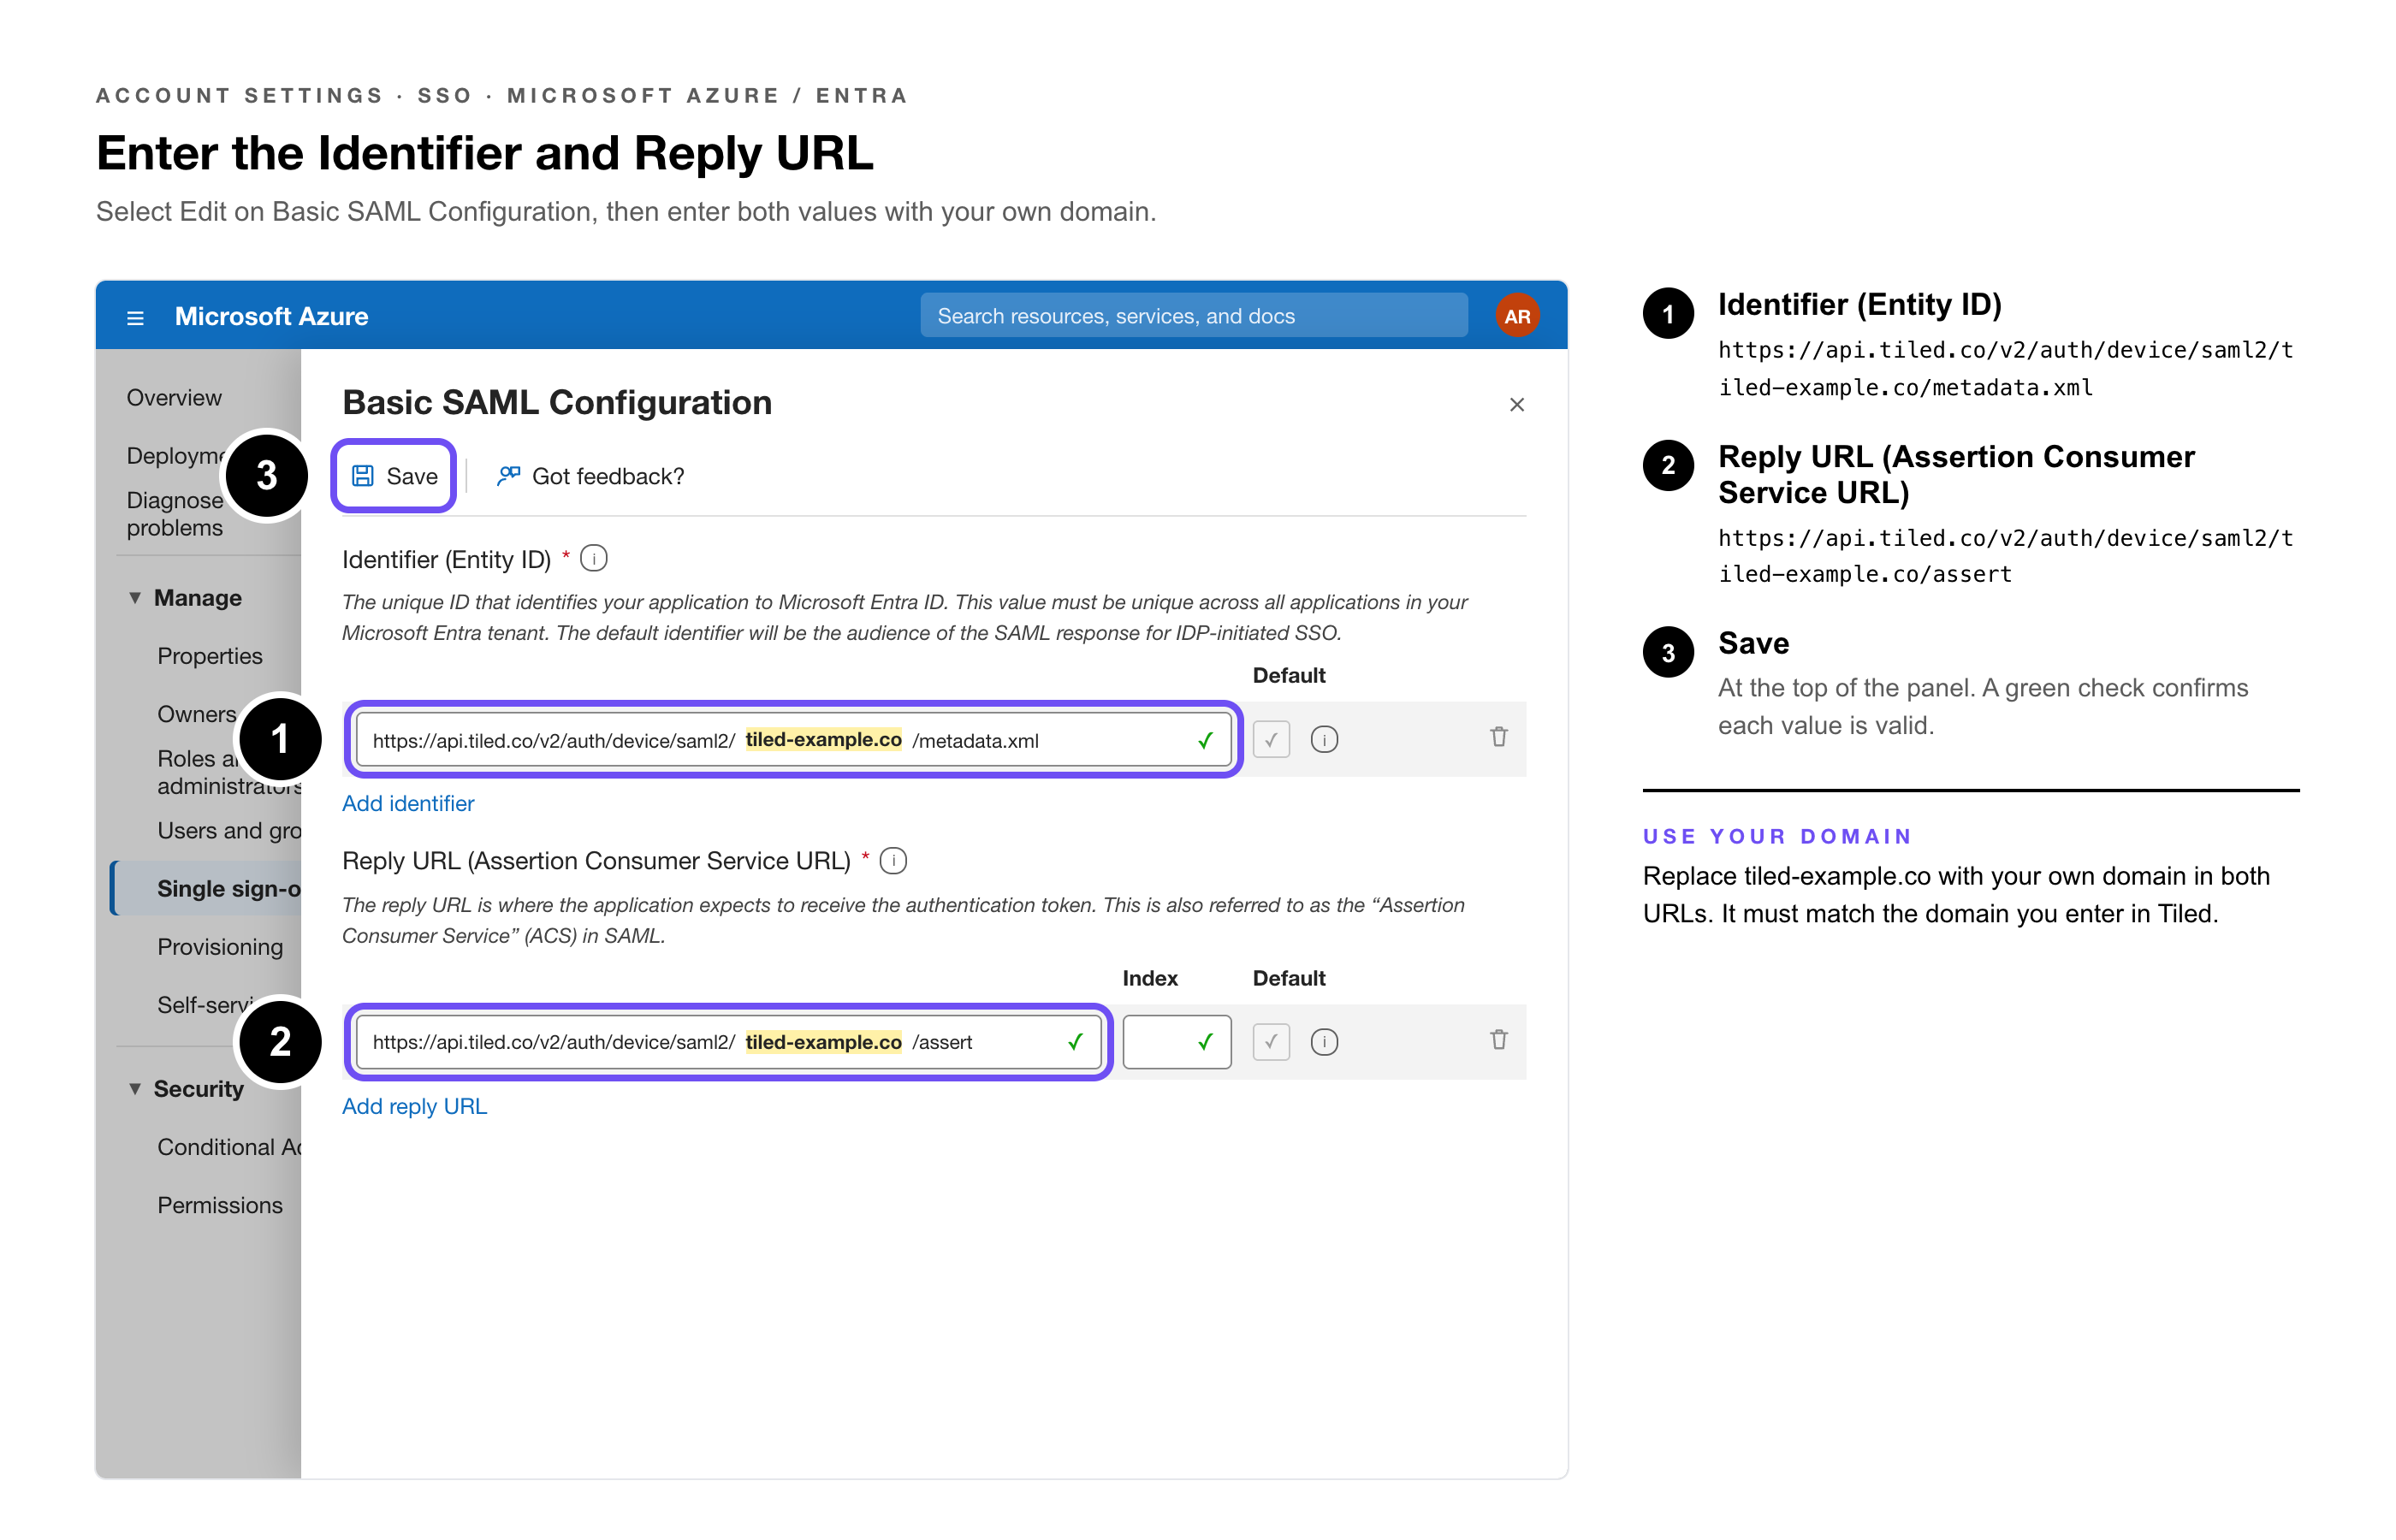
3. Save — the Basic SAML Configuration.
Add the name and email claims
|
Heads Up: Sign-in fails without these two claims. The source attribute depends on how your directory is set up, so check which attribute holds each value for your users. |
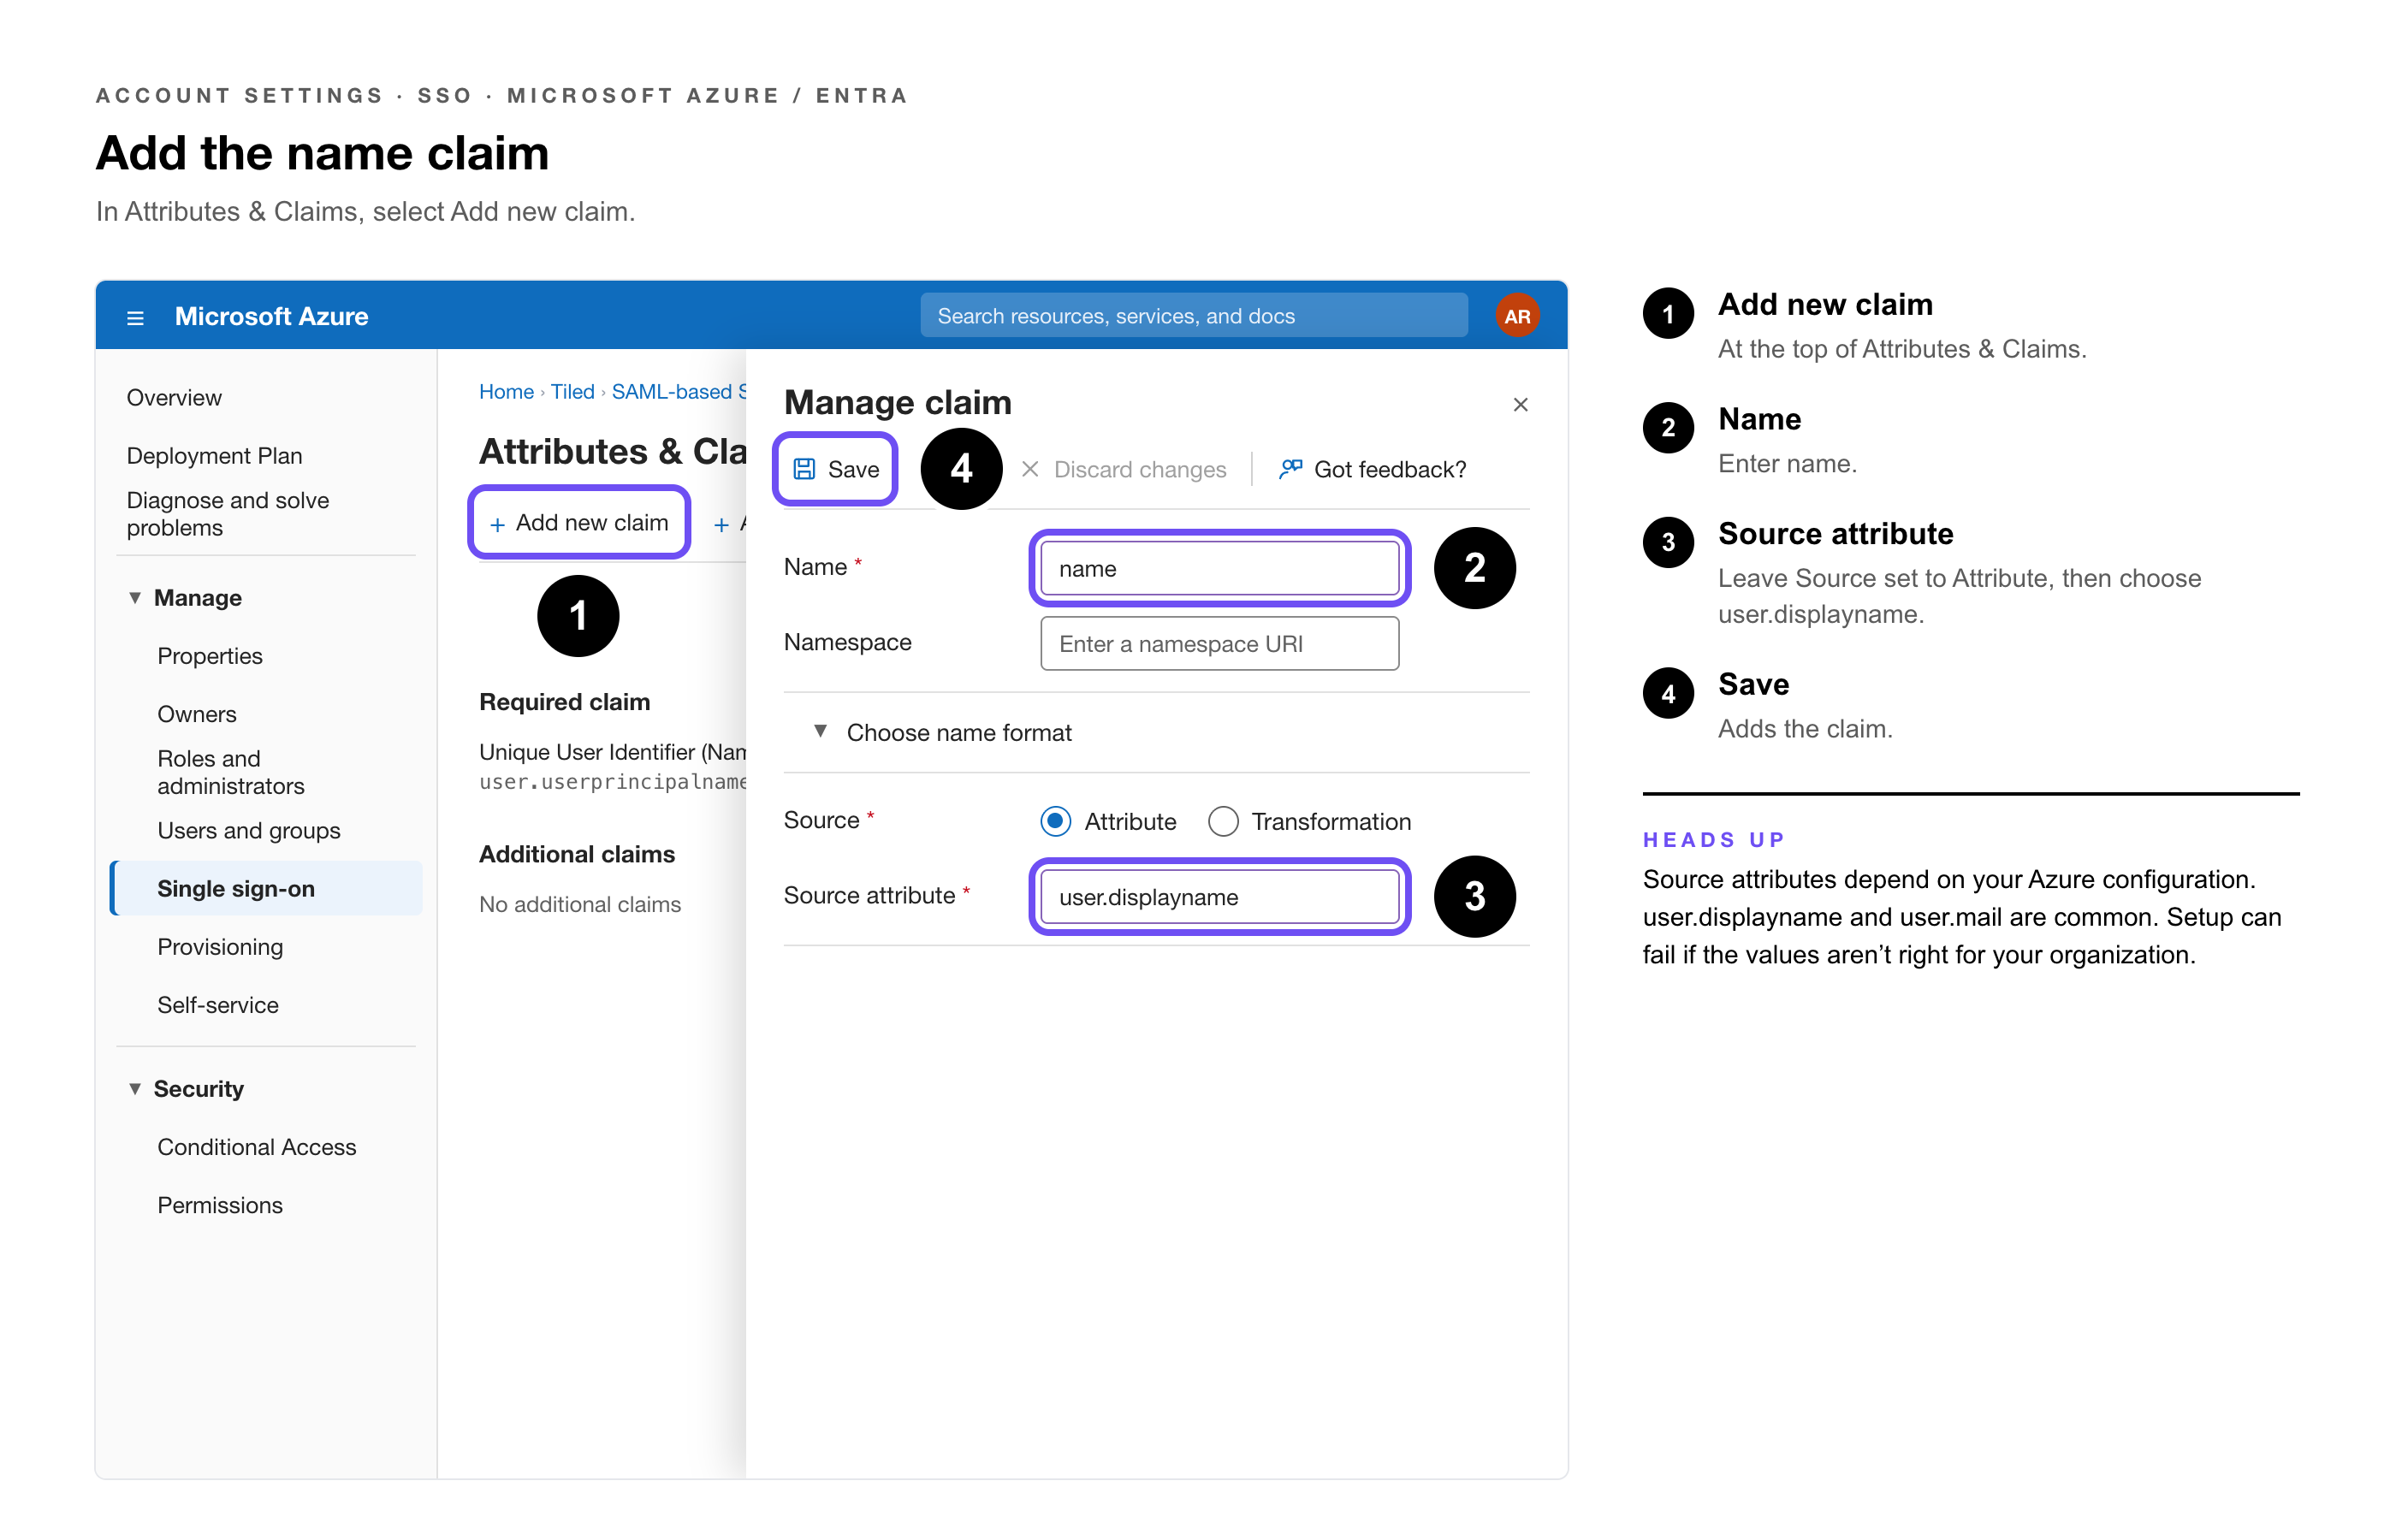
1. Edit Attributes & Claims — and select Add new claim.
2. Add a claim named name — with the source attribute that holds each person’s full name. A common choice is user.displayname.
3. Add a claim named email — with the source attribute that holds each person’s email address. A common choice is user.mail.
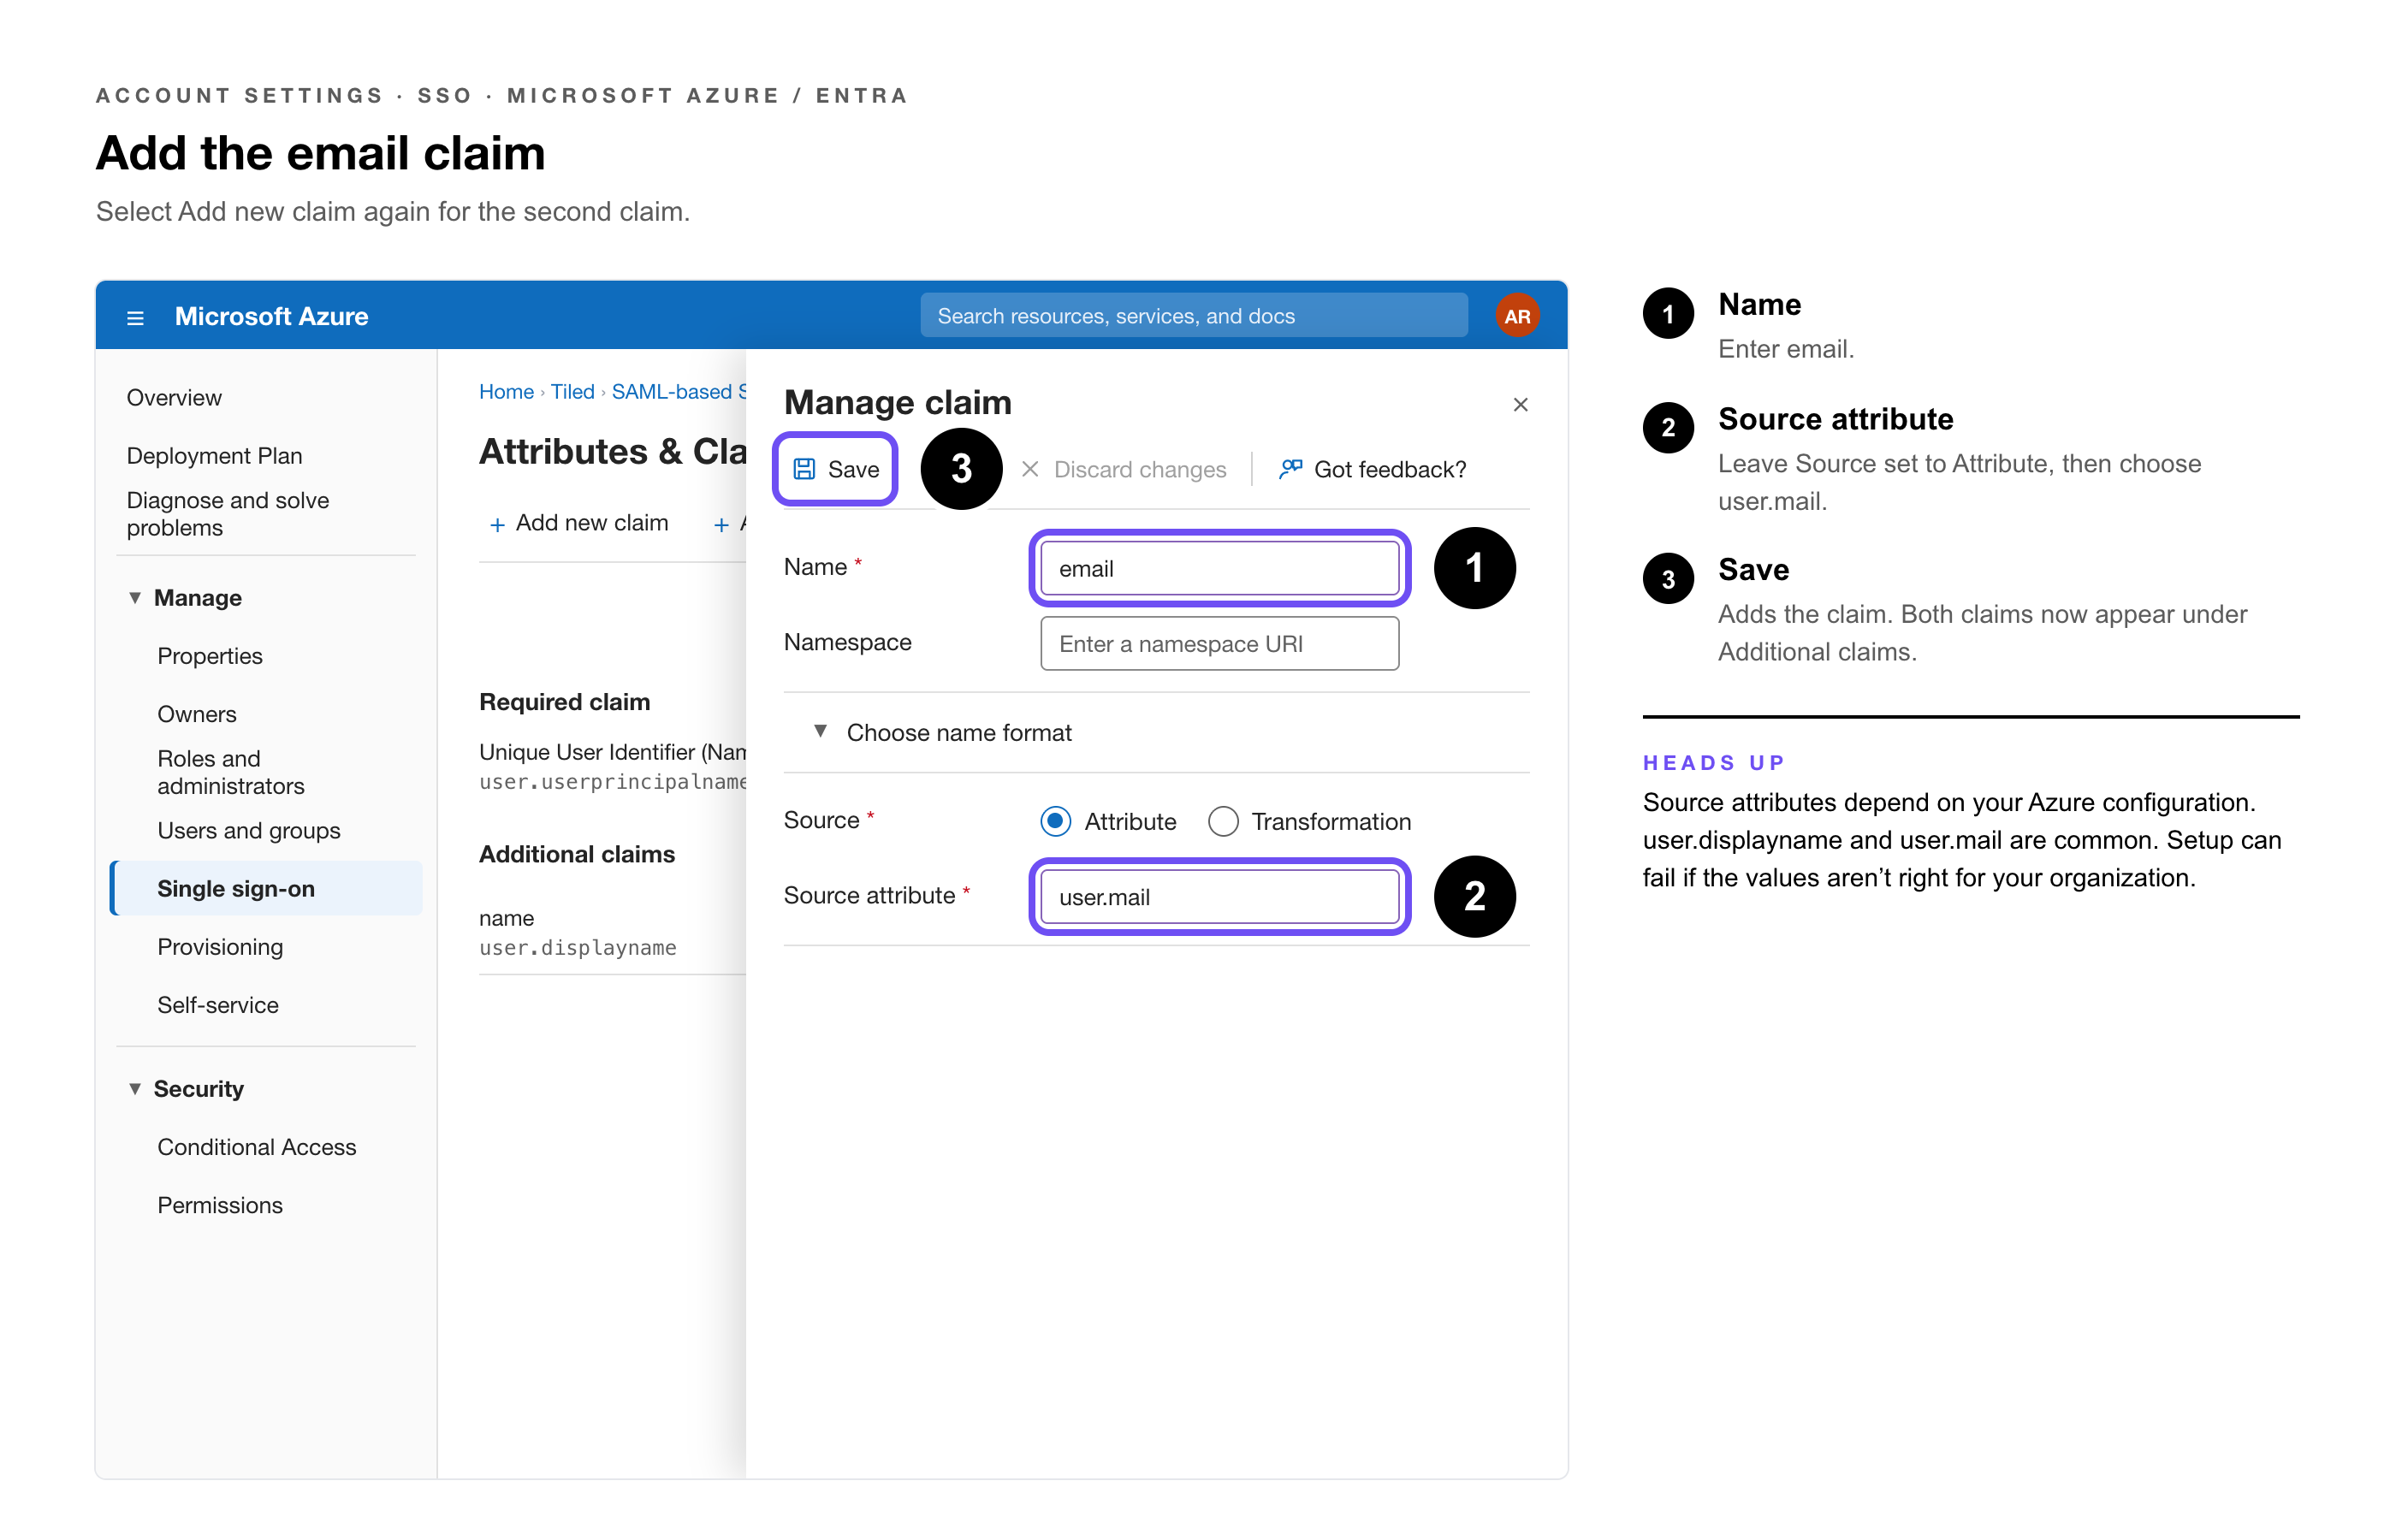
4. Leave Namespace blank — for both claims, and save.
|
Claim |
Suggested Source Attribute |
If It Doesn’t Work |
|
name |
user.displayname |
Use user.givenname and user.surname, or another attribute your directory fills in. |
|
|
user.mail |
If some users have no mailbox, user.mail may be empty. Use user.userprincipalname if it matches their email address. |
Download the metadata
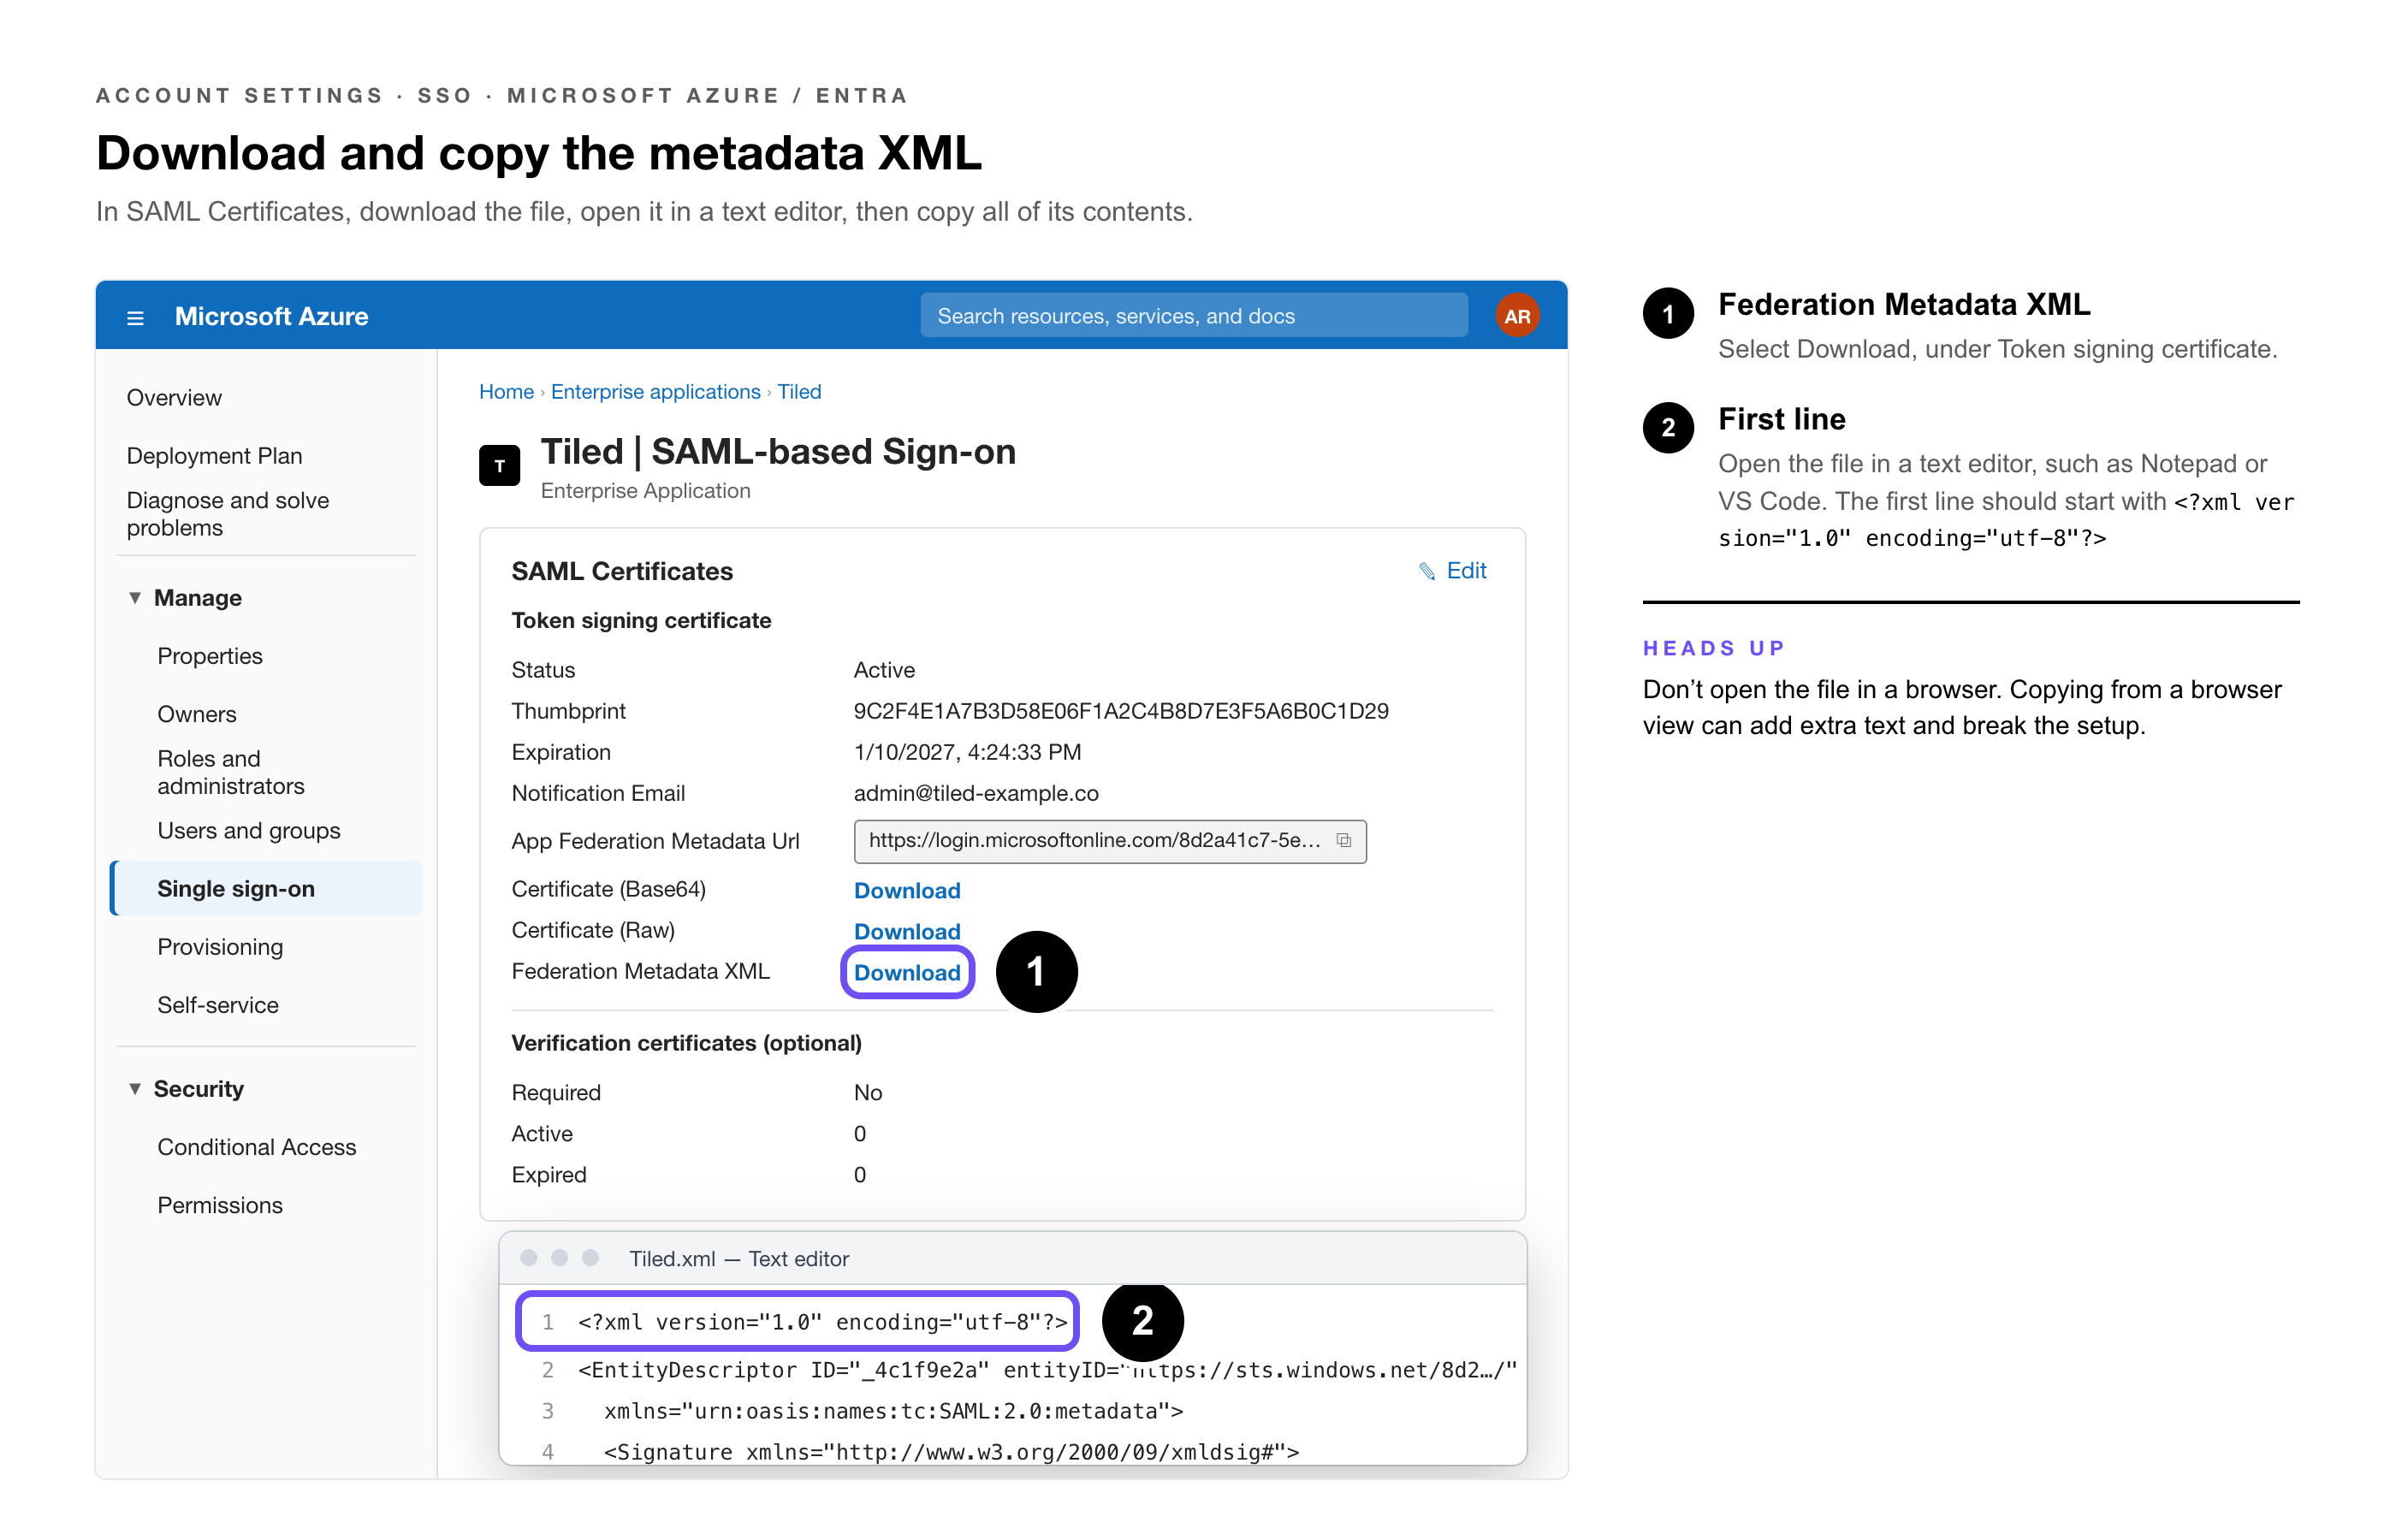
1. Under SAML Certificates, — download Federation Metadata XML.
2. Open the file in a text editor, — such as Notepad or VS Code, not in a browser. The first line starts with <?xml version="1.0" encoding="utf-8"?>.
3. Copy the entire contents. — You’ll paste them into Tiled.
Part 2: Connect Entra ID in Tiled
1. In Tiled, open Settings — and select General.
2. Under single sign-on, select Enable SSO, — then open the SAML tab.
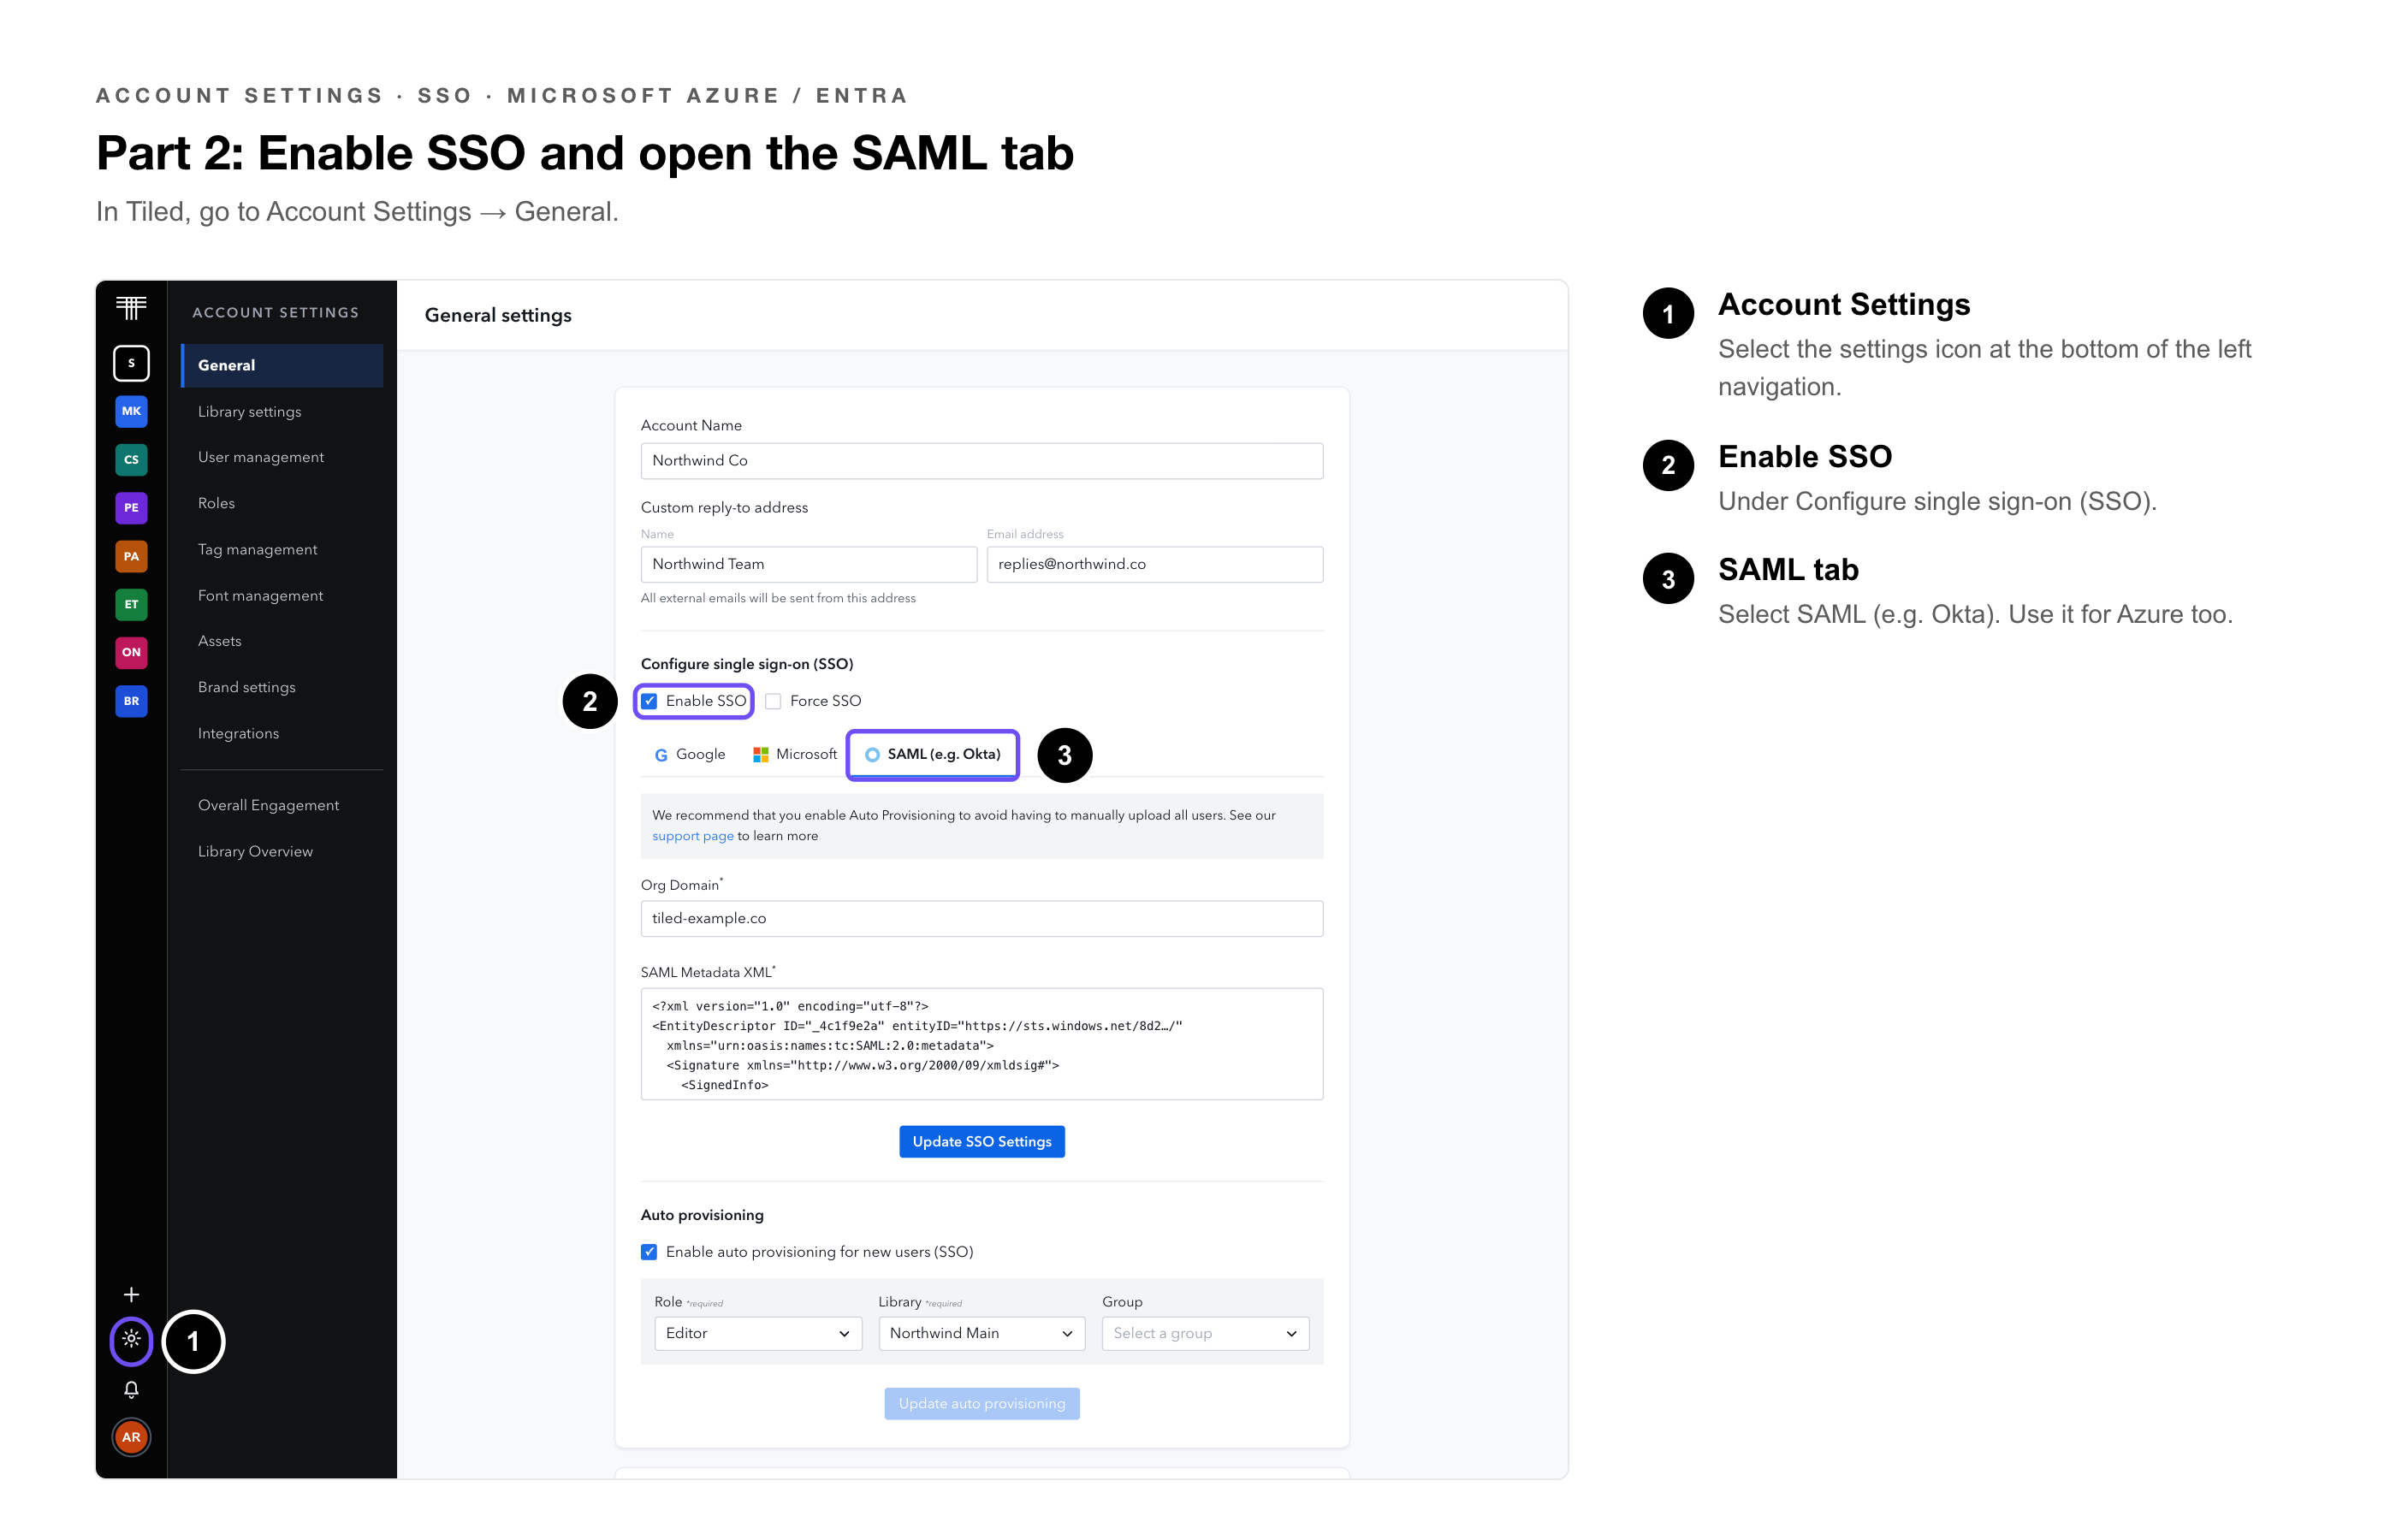
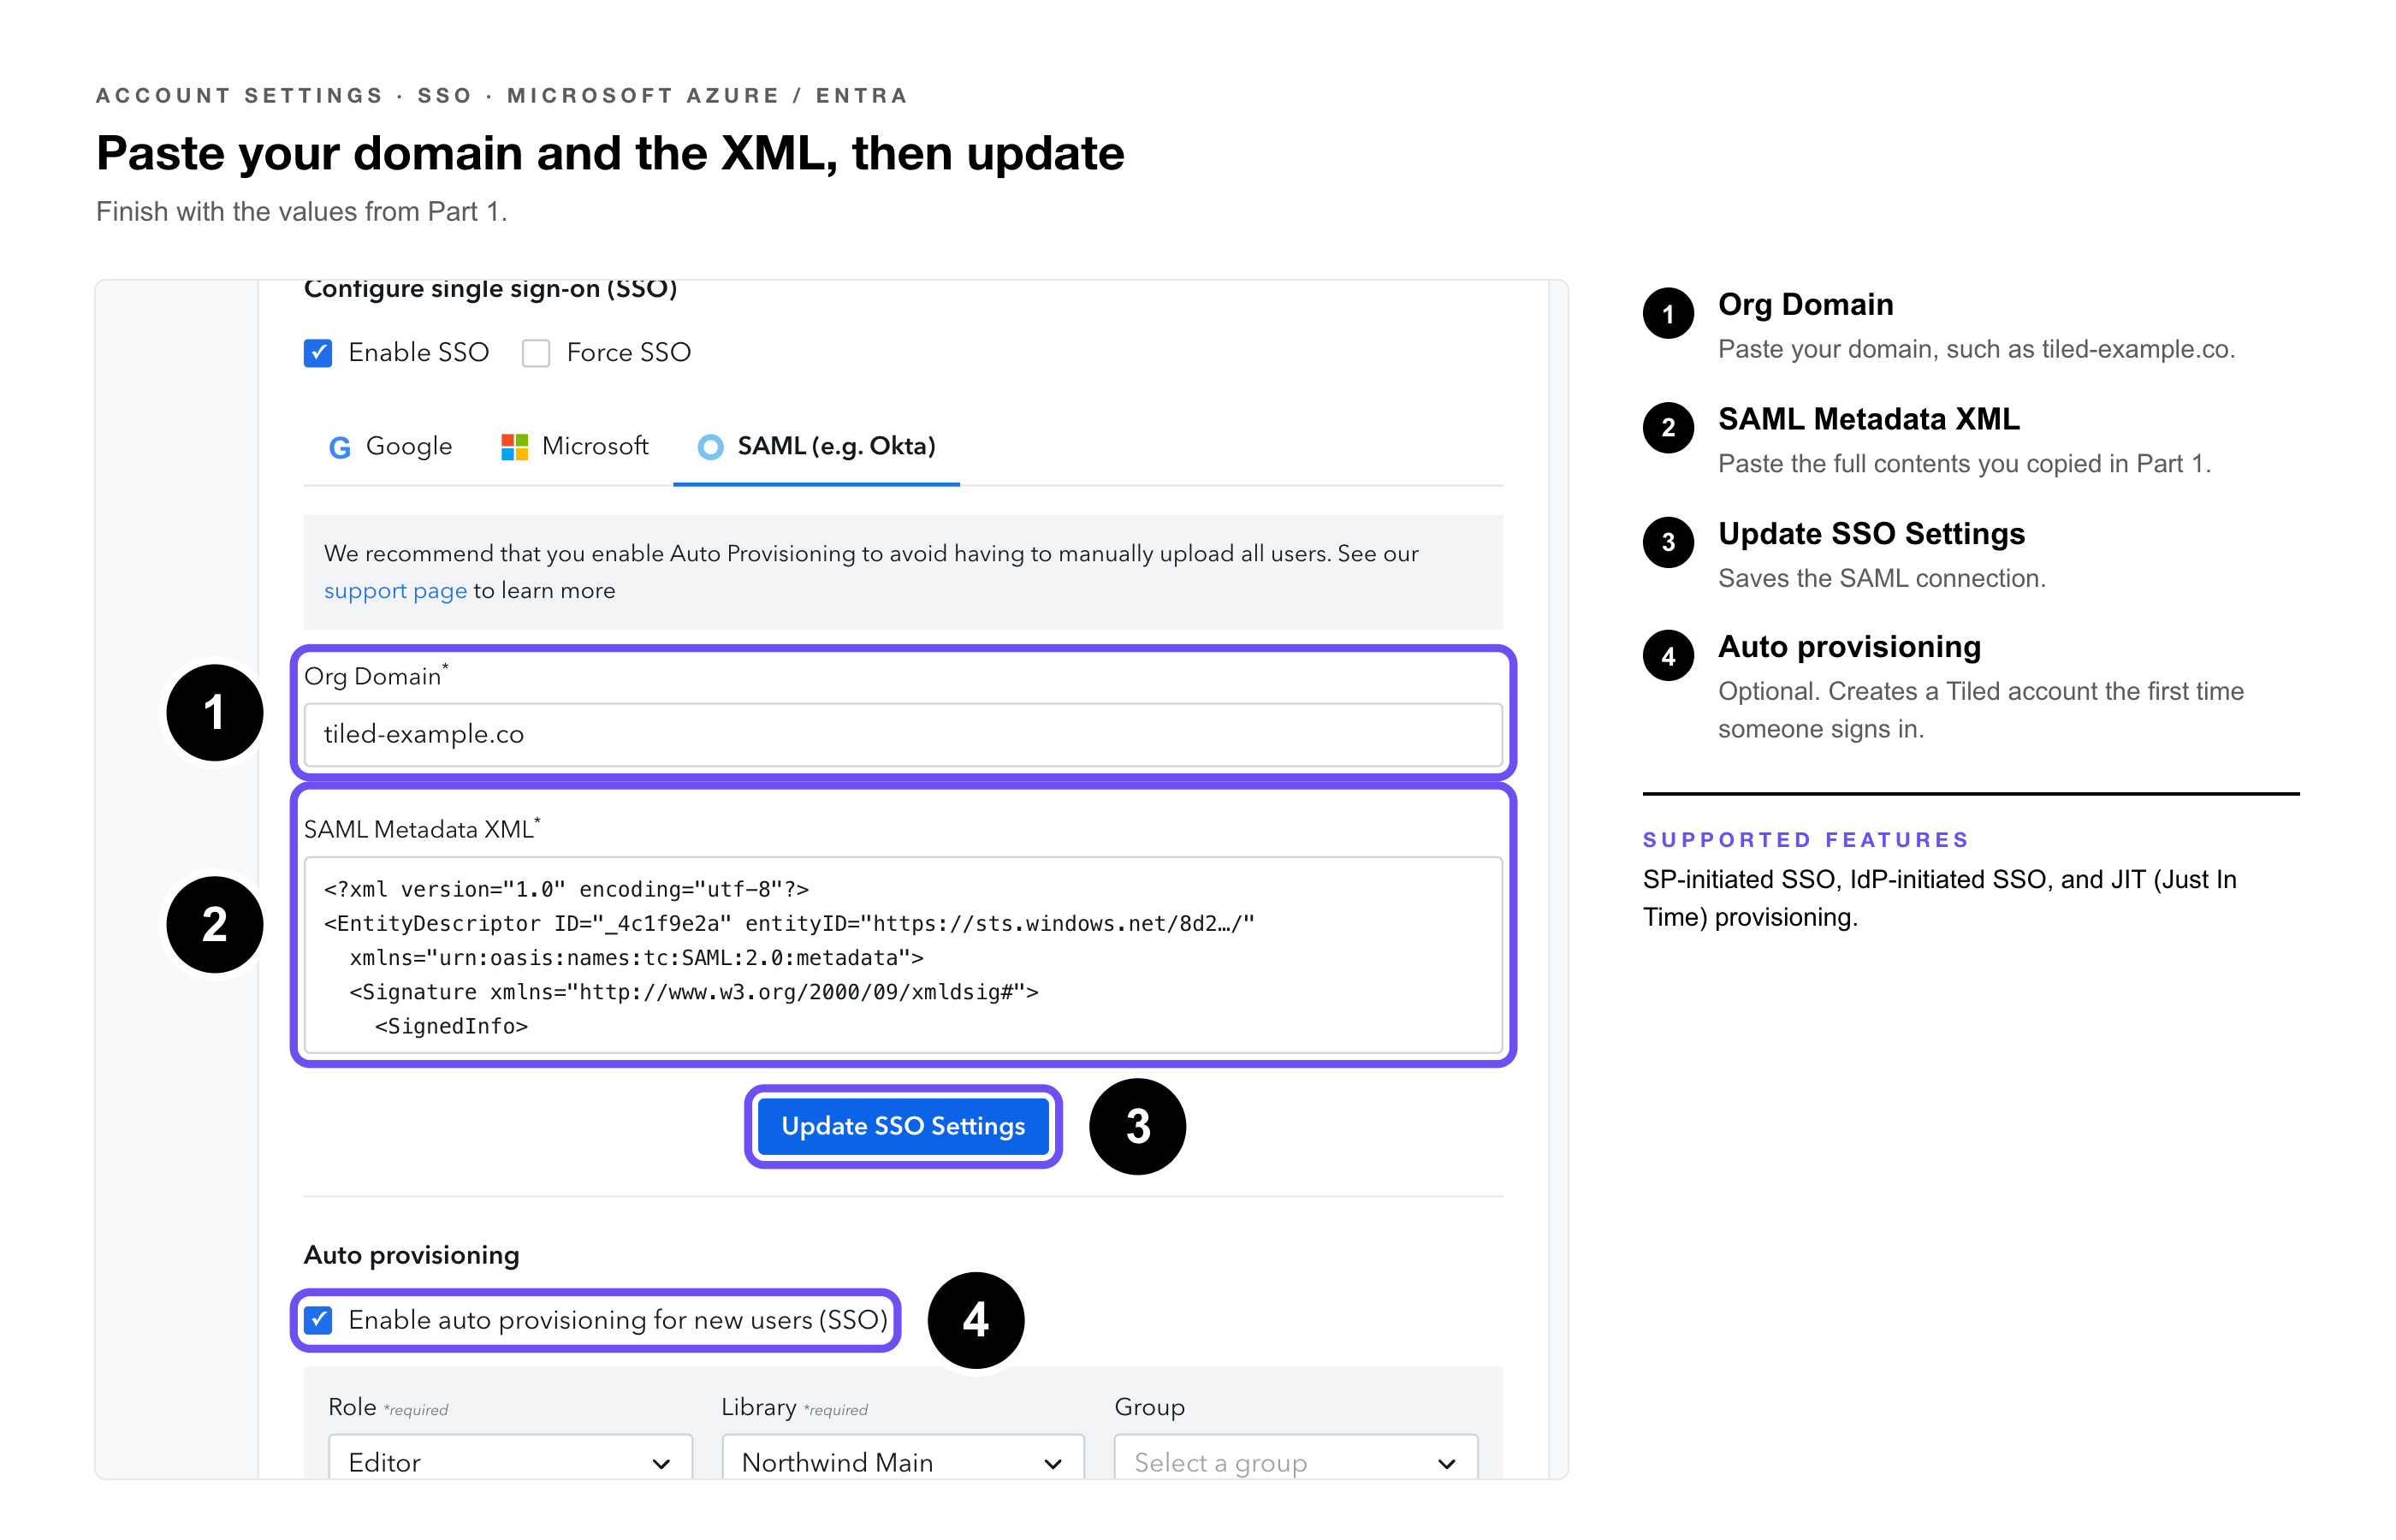
3. Enter your own sign-in domain, — such as tiled-example.com. (Make sure is your organization domain)
4. Paste the metadata XML — you copied from Entra ID.
5. Select Update SSO Settings. — SSO is now available to people assigned in Entra ID.
Optional: create accounts automatically
Turn on Auto provisioning to create a Tiled account the first time an assigned person signs in. Choose the Default Role, Default Library, and Default Group they’ll get. You can change each person’s access later in User Management.
|
Pro Tip: Use the lowest role most people need, usually Base, as the Default Role, and raise individual users afterward. |
Test Before You Require SSO
1. Leave SSO on Enable SSO, — not Force SSO, so people can still use passwords while you test.
2. Sign in as an assigned test user — from a private browser window, entering your sign-in domain.
3. Check the result: — the user lands in the right library with the right role, and their name and email are correct.
4. Switch to Force SSO — only when testing succeeds.
|
Heads Up: With Force SSO on, password sign-in is turned off for everyone. A mistake in the Entra ID setup would then stop people signing in, so always test with Enable SSO first. |
Supported Sign-In Flows
|
Flow |
How It Works |
|
SP-initiated |
People start at Tiled, enter your domain, and sign in with Microsoft. |
|
IdP-initiated |
People start from the Tiled tile in My Apps, Microsoft’s app launcher. |
|
Just-in-time provisioning |
With Auto provisioning on, Tiled creates the account at first sign-in. |
Keeping SSO Working: Certificate Renewal
Entra ID signs SAML sign-ins with a certificate that is valid for three years by default. Microsoft emails the addresses on the app’s notification list 60, 30, and 7 days before it expires. If it expires, nobody can sign in with SSO.
1. Before it expires, in Entra ID open the app’s Single sign-on page — and edit SAML Certificates.
2. Create a new certificate — and save it.
3. Make the new certificate active, — then download the Federation Metadata XML again.
4. Paste the new metadata into Tiled — on the SAML tab and select Update SSO Settings. Test sign-in straight away.
|
Pro Tip: Add a shared mailbox or distribution list to the certificate’s notification list, so renewal warnings don’t depend on one person. |
Troubleshooting
|
Problem |
Check |
|
Sign-in fails right after Microsoft |
The name and email claims exist, are spelled exactly, and have no namespace. |
|
A user can’t sign in but others can |
They’re assigned to the app in Users and groups, directly or through a group. |
|
Email is missing or wrong in Tiled |
The email claim’s source attribute. Try user.userprincipalname if user.mail is empty. |
|
Error about the identifier or reply URL |
Both URLs use your exact sign-in domain, with no typos or extra slashes. |
|
Everyone stopped being able to sign in |
The SAML certificate may have expired. Renew it and paste the new metadata into Tiled. |
|
New users don’t get accounts |
Auto provisioning is on, with a Default Role, Library, and Group selected. |
|
Email Address Case Sensitivity |
Please verify whether email addresses are case-sensitive during the email verification process. Both Microsoft and Tiled may treat uppercase and lowercase characters differently, so we’d like to confirm that the casing is handled correctly and consistently. |
|
XML Error |
Make sure there are not empty spaces at the beginning or the end of the pasted XML file. |
|
Try It Yourself: Assign one test account to the app, sign in through My Apps and then from the Tiled login screen, and confirm both work before assigning everyone else. |
|
Common Questions
|
Question |
Answer |
|
Do I need this to use Sign in with Microsoft? |
No. Sign in with Microsoft works without setup. SAML SSO is for central control, required SSO, and automatic account creation. |
|
Can two Tiled accounts use the same domain? |
No. Each sign-in domain must be unique to one Tiled account. |
|
What’s the difference between Enable SSO and Force SSO? |
Enable SSO lets people use SSO or a Tiled password. Force SSO allows SSO only. |
|
What happens when someone leaves the company? |
Remove or disable them in Entra ID and they can no longer sign in to Tiled with SSO. |
|
Using a different identity provider? |
See Configure SSO for Google or Configure SSO for Okta, or submit a ticket at support.tiled.co. |
Microsoft Resources
• Add an enterprise application
• Enable SAML single sign-on for an enterprise application
• Assign users and groups to an application
• Manage certificates for federated single sign-on
Related Articles
• Account Settings: General — Enable and Force SSO, auto provisioning, and share link defaults.
• What is Single Sign-On (SSO)? — How SSO works with Tiled.
• Configure SSO for Google — Google Workspace setup.
• Configure SSO for Okta — Okta setup.
• Account Settings: User Management — Reviewing roles and library access after sign-in.